
[2025年11月] 最新のPCNSE PCNSE日本語試験解答豪華セット問題集
Palo Alto NetworksコンテンツをマスターしてPCNSE日本語試験合格保証つき問題集!
質問 # 18
管理者は、パロアルト ネットワーク ファイアウォールでアドバンス ルーティング エンジンを有効にする方法を教えてください。
- A. [デバイス] > [セットアップ] > [セッション] > [セッション設定] で高度なルーティング エンジンを有効にし、コミットして再起動します。
- B. [ネットワーク] > [仮想ルーター] > [再配布プロファイル] で高度なルーティングを有効にしてから、コミットします。
- C. [ネットワーク] > [仮想ルーター] > [ルーター設定] > [全般] で高度なルーティングを有効にし、コミットして再起動します。
- D. [デバイス] > [セットアップ] > [管理] の [一般設定] で [高度なルーティング] を有効にし、コミットして再起動します。
正解:C
解説:
Explanation
Enable Advanced Routing in Network > Virtual Routers > Router Settings > General, then commit and reboot
1. This means that the administrator can enable advanced routing features such as RIB filtering, BFD, multicast, and redistribution profiles for each virtual router on the firewall. The firewall requires a reboot after enabling advanced routing to apply the changes.
質問 # 19
管理者は 4 つの新しいリモート オフィスを企業データ センターに接続します。管理者は、パロアルトネットワークの次世代ファイアウォールで大規模 VPN (LSVPN) 機能を使用することにしました。
サイトを接続するには管理者は何を設定する必要がありますか?
- A. IKE ゲートウェイ
- B. SD-WAN
- C. ジェネリック ルーティング カプセル化 (GRE) トンネル
- D. GlobalProtect サテライト
正解:D
解説:
For remote offices to the corporate data center (Hub and Spoke Topology), we need GlobalProtect Satellite connected to the GP Gateway.
https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-admin/large-scale-vpn-lsvpn
質問 # 20
トランスポート モードの IPSec に必要な 2 つはどれですか (2 つ選択してください)。
- A. DHグループ20(ECP-384ビット)
- B. 自動生成されたキー
- C. NATトラバーサル
- D. IKEv1
正解:A、D
質問 # 21 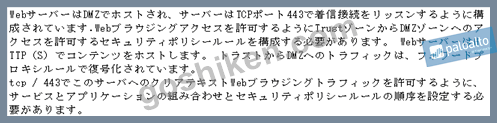
- A. Rule #1: application: web-browsing; service: service-https; action: allowRule #2: application: ssl; service: application-default; action: allow
- B. Rule # 1: application: ssl; service: application-default; action: allowRule #2: application: web-browsing; service: application-default; action: allow
- C. Rule #1: application: web-browsing; service: application-default; action: allowRule #2: application: ssl; service: application-default; action: allow
- D. Rule #1: application: web-browsing; service: service-http; action: allowRule #2: application: ssl; service: application-default; action: allow
正解:C
質問 # 22
リモート管理者は、信頼できないインターレースでファイアウォールにアクセスする必要があります。安全な管理アクセスのために、インターフェイス管理プロファイルに構成する3つのオプションはどれですか。 (3つ選択してください)
- A. ユーザーID
- B. HTTPS
- C. SSH
- D. HTTP
- E. 許可されたIPアドレス
正解:B、C、E
質問 # 23
セキュリティ エンジニアは、ファイアウォールのインターネット対応インターフェイスの背後にある一連のサーバーで発生するパケット フラッドを軽減する必要があります。
これらのパケット フラッドを防ぐには、どのセキュリティ プロファイルをポリシーに適用する必要がありますか?
- A. 脆弱性保護プロファイル
- B. データフィルタリングプロファイル
- C. DoS 保護プロファイル
- D. URL フィルタリング プロファイル
正解:C
質問 # 24
Panorama からの次の画像では、一部の値が赤で表示されているのはなぜですか?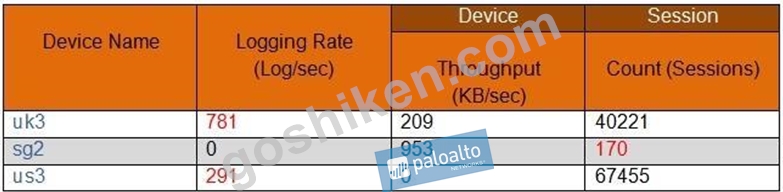
- A. sg2 のセッションしきい値が正しく構成されていません。
- B. us3 のログ記録レートは、管理者が設定したしきい値から外れています。
- C. sg2 セッション数は、他の管理対象デバイスと比較して最も少なくなります。
- D. uk3 のログ記録率は、7 日間の計算されたベースラインから外れています。
正解:D
解説:
https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-web-interface-help/panorama-web- interface/panorama-managed-devices-summary/panorama-managed-devices-health A metric health baseline is determined by averaging the health performance for a given metric over seven days plus the standard deviation.
質問 # 25
エンジニアは、パノラマで共通の構成を持つ複数のファイアウォールを展開しています。
ネストされたデバイス グループを使用する利点を 2 つ選んでください。(2つ選んでください。)
- A. すべてのセキュリティ ポリシー ルールとオブジェクトを継承します。
- B. 親のセキュリティ ポリシー ルールとオブジェクトを継承する
- C. IPSec 暗号化プロファイルを継承する
- D. 共有グループから設定を継承
正解:B、D
解説:
Explanation
https://docs.paloaltonetworks.com/panorama/9-1/panorama-admin/panorama-overview/centralized-firewall-conf
質問 # 26
ファイアウォール エンジニアは、インターネットからエッジ ファイアウォールの背後でホストされている Web サーバーへのトラフィックを許可する宛先静的 NAT ルールを作成します。サーバーの NAT 前の IP アドレスは 153.6 12.10、NAT 後の IP アドレスは 192.168.10.10 です。以下のルーティングとインターフェイスの情報を参照してください。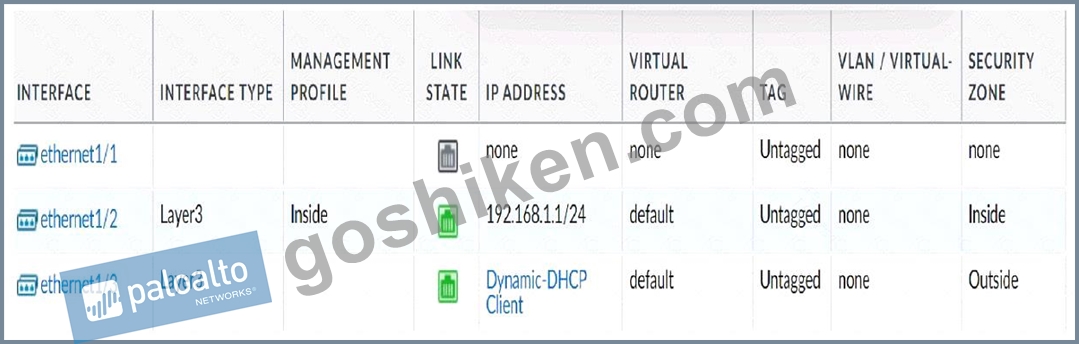
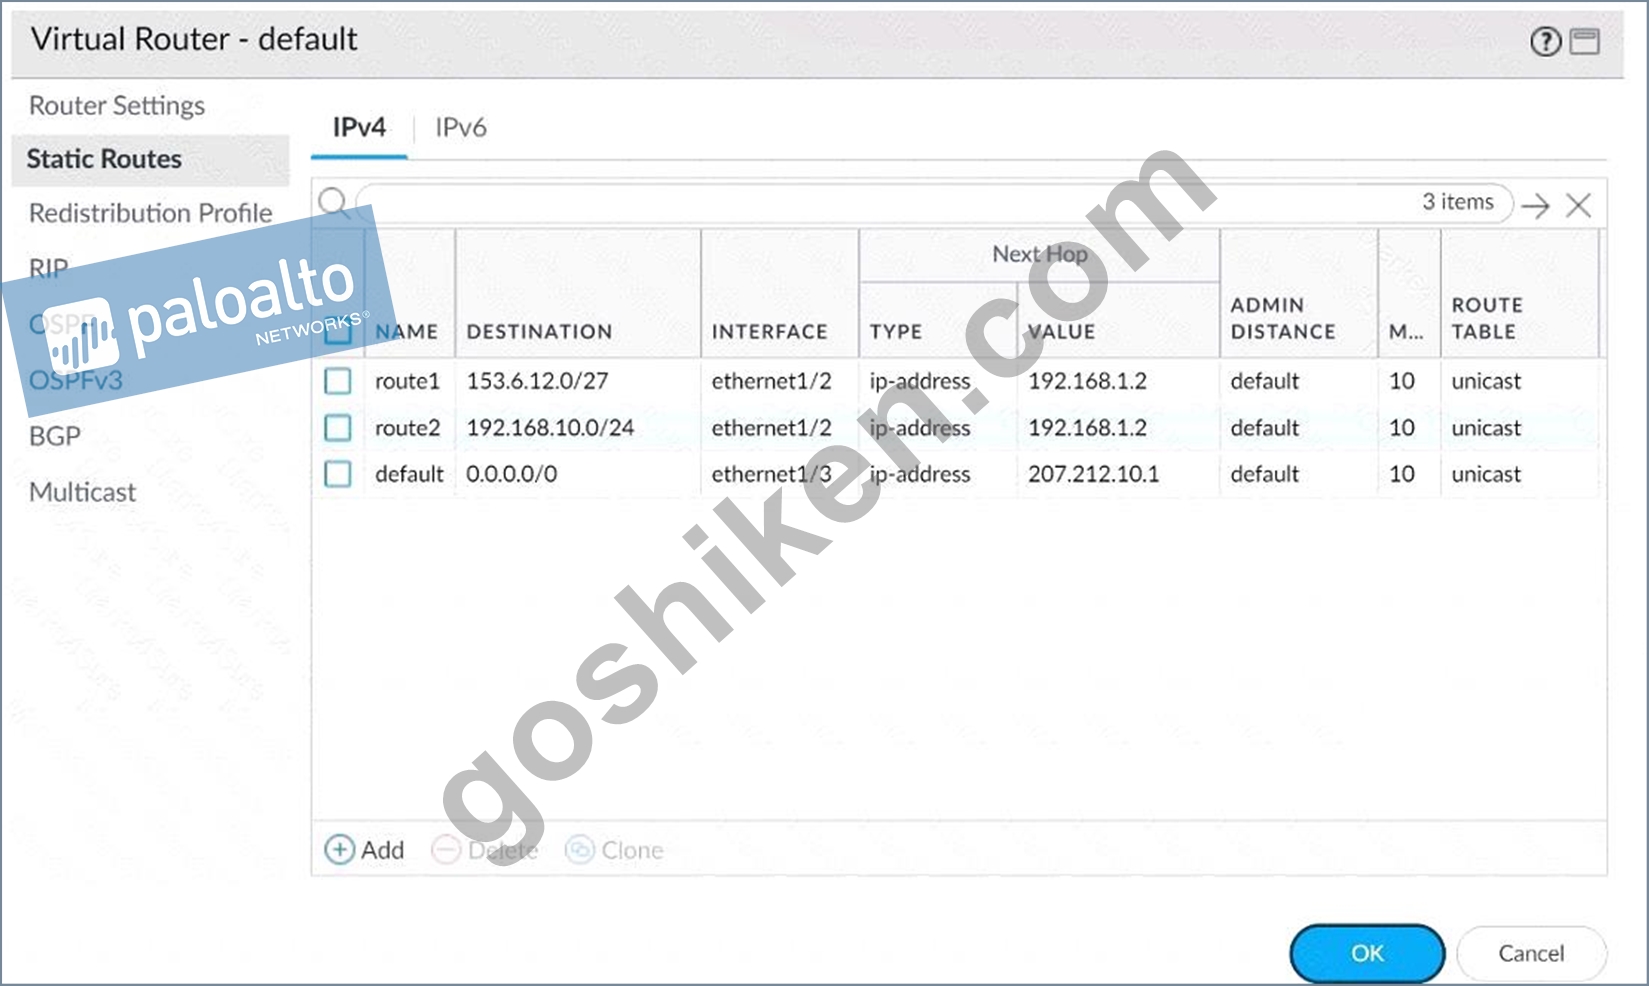
NAT ルールの宛先ゾーンは何に設定する必要がありますか?
- A. DMZ
- B. 内部
- C. なし
- D. 外側
正解:D
解説:
https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-networking-admin/nat/nat-configuration-examples/destina
質問 # 27
ファイアウォールでは、どの 3 つの復号化方法が有効ですか? (3つお選びください)
- A. SSL インバウンド検査
- B. SSL アウトバウンド プロキシレス検査
- C. SSL インバウンド プロキシ
- D. SSH プロキシ
- E. 復号化ミラー
正解:A、D、E
解説:
You can also use Decryption Mirroring to forward decrypted traffic as plaintext to a third party solution for additional analysis and archiving.
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/decryption/decryption- overview.html#idd71f8b4d-cd40-4c6c-905f-2f8c7fca6537
https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/decryption/decryption-overview
質問 # 28
デバイス > ログ設定でどの 2 つのログ タイプの転送が設定されます? (2 つ選択してください)
- A. 脅威
- B. ヒップマッチ
- C. トラフィック
- D. 構成
正解:B、D
解説:
Based on PAN-OS 11.0 documentation, the forwarding configuration for specific log types in Device > Log Settings involves selecting log types for system-level logs, which include HIP Match and Configuration logs.
Explanation for Each Option
A: Threat
* Threat logs record detected security threats such as malware, viruses, and vulnerabilities.
* Forwarding of Threat logs is not configured in Device > Log Settings. Instead, Threat logs are forwarded using Log Forwarding Profiles applied to Security Policies.
* Verdict: Incorrect.
B: HIP Match
* HIP Match logs capture information about endpoint compliance reported by GlobalProtect clients.
* These logs can be configured for forwarding in Device > Log Settings for monitoring and compliance purposes.
* Verdict: Correct.
C: Traffic
* Traffic logs provide details about allowed or denied network traffic.
* Forwarding of Traffic logs is configured using Log Forwarding Profiles applied to Security Policies, not in Device > Log Settings.
* Verdict: Incorrect.
D: Configuration
* Configuration logs track administrative changes to the firewall, such as updates to policies, settings, and objects.
* These logs can be forwarded from Device > Log Settings for auditing purposes.
* Verdict: Correct.
Correct Answer
B: HIP Match
D: Configuration
Key Points from PAN-OS 11.0 Documentation
* Device > Log Settings is specifically for system-related logs like HIP Match and Configuration.
* Logs like Threat and Traffic are handled through Log Forwarding Profiles applied to Security or NAT policies.
Documentation Reference
For further details, refer to the official Palo Alto Networks PAN-OS 11.0 Admin Guide under Device > Log Settings. This section outlines which log types can be forwarded from this menu.
質問 # 29
テンプレートで構成できる 2 つのオブジェクトはどれですか? (2つお選びください。)
- A. アプリケーショングループ
- B. SD-WAN パス品質プロファイル
- C. IPsec トンネル
- D. モニタープロファイル
正解:C、D
解説:
https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-web-interface-help/network/network-network-profiles/network-network-profiles-monitor.html
質問 # 30
セキュリティ優先のネットワークで、コンテンツの更新を動的に更新するための推奨しきい値はどれくらいですか?
- A. 36時間
- B. 6〜12時間
- C. 24時間
- D. 1〜4時間
正解:B
解説:
Explanation
https://docs.paloaltonetworks.com/pan-os/8-1/pan-os-admin/threat-prevention/best-practices-for-content-and-thre
質問 # 31 
- A. SMTP Inbound Decryption
- B. TLS Bidirectional Inspection
- C. SSL Inbound Inspection
- D. SSH Forward Proxy
正解:C
解説:
Reference:
https://www.paloaltonetworks.com/documentation/71/pan-os/pan-os/decryption/configure-ssl-inbound-inspectio
質問 # 32
ベスト プラクティス評価に関して正しいのはどれですか?
- A. 現在の構成がパロアルトネットワークの推奨事項とどのように比較されるかを示します。
- B. ネットワークとセキュリティ アーキテクチャのすべての領域にわたるセキュリティ リスク防止のギャップを明らかにするのに役立つ一連のアンケートを提供します。
- C. ファイアウォール上でのみ実行されます
- D. 認定セールス エンジニアの指導を受けると、予防活動に重点を置く必要がある最大のリスク領域を特定するのに役立ちます。
正解:A
解説:
The Best Practice Assessment (BPA) tool compares the configuration of firewalls and Panorama to the Palo Alto Networks best practice recommendations. Run the BPA periodically to identify security weaknesses, see the best practice settings, and implement them to improve your security posture.
https://docs.paloaltonetworks.com/best-practices/10-2/bpa-getting-started
質問 # 33
ファイアウォール管理者は、会社のファイアウォールでのパケット バッファの使用率が高いことを調査しています。脅威ログを調べ、ファイアウォールによってドロップされる単一のソースからの多数のフラッド攻撃を確認した後、管理者は、同様の攻撃から保護するためにパケット バッファー保護を有効にすることを決定します。
管理者はファイアウォールでパケット バッファ保護をグローバルに有効にしていますが、それでもパケット バッファの使用率が高いことがわかります。
パケット バッファのオーバーフローを防ぐために、管理者は他に何をする必要がありますか?
- A. 影響を受けるゾーンのパケット バッファ保護を有効にします。
- B. 外部からのトラフィックを許可するセキュリティ ルールに DOS プロファイルを適用します。
- C. 影響を受けるゾーンにゾーン保護プロファイルを追加します。
- D. 外部からのトラフィックを許可するすべてのセキュリティ ルールに、デフォルトの脆弱性保護プロファイルを追加します。
正解:C
解説:
When facing high packet buffer utilization due to flood attacks, enabling packet buffer protection is a strategic step. However, simply enabling it globally might not be sufficient. The additional step needed is:
D: Add a Zone Protection profile to the affected zones:Zone Protection profiles provide a set of protections against various flood types, reconnaissance attempts, packet-based attacks, and protocol anomalies. By adding a Zone Protection profile to the zones that are experiencing high packet buffer utilization, the firewall can apply specific thresholds and actions to mitigate flood attacks, thus preventing the packet buffers from being overwhelmed.
It's important to configure the Zone Protection profile with appropriate thresholds and actions for flood protection, taking into consideration the normal traffic patterns and the capacity of the network and firewall.
This proactive approach ensures that legitimate traffic is allowed while mitigating potential attacks that could consume excessive resources.
For comprehensive instructions on setting up Zone Protection profiles and configuring them for optimal protection against flood and other types of attacks, refer to the Palo Alto Networks knowledge base and official documentation. These resources provide valuable insights into best practices and recommendations for securing your network infrastructure.
質問 # 34
PAN-OS®ソフトウェアとのネイティブ統合がない802.1x対応のワイヤレスネットワークデバイスを介して接続するユーザーのユーザー名にIPアドレスをマップするユーザーIDの方法はどれですか?
- A. ポートマッピング
- B. サーバー監視
- C. クライアントプロービング
- D. XML API
正解:D
解説:
https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/user-id/user-id-concepts/user-mapping/xml-api.html
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/user-id/user-id-concepts/user-mapping/server-monitoring.html
質問 # 35 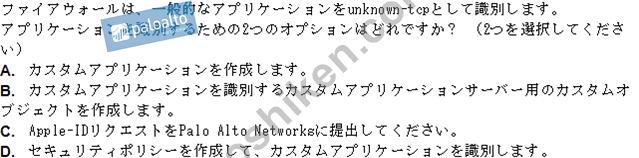
- A. Option A
- B. Option C
- C. Option B
- D. Option D
正解:A
質問 # 36
......
あなたを合格させるPalo Alto Networks PCNSE日本語試験専門問題集はここにある:https://www.goshiken.com/Palo-Alto-Networks/PCNSE-JPN-mondaishu.html