

PDFを無料でダウンロードには300-710有効な練習テスト問題があります
300-710テストエンジンお試しセット、300-710問題集PDF
Cisco 300-710認定試験は、Cisco Firepowerでネットワークを保護するための専門知識を実証したいIT専門家にとって非常に価値のある認定です。この認定は、最新のセキュリティの脅威を軽減し、ネットワークインフラストラクチャを保護するために必要な知識とスキルを検証します。試験に合格するには、候補者は、ネットワークセキュリティの概念、脅威防衛技術、および火力管理と構成を確実に理解している必要があります。
Cisco Firepowerテクノロジーは、包括的なセキュリティサービスをネットワークに提供するために設計された一連の高度なセキュリティソリューションです。これらのテクノロジーには、ネットワークを様々なセキュリティ脅威から保護するために使用されるFirepower Threat Defense(FTD)およびFirepower Management Center(FMC)ソリューションが含まれています。Cisco 300-710試験は、これらのテクノロジーの知識とネットワークを効果的に保護する能力をテストするために設計されています。
Cisco 300-710試験は、約65〜75の質問で構成される90分間の試験です。この試験は英語と日本の言語で入手でき、ピアソンvueテストセンターで世界中で撮影できます。この試験では、Cisco Firpower NGIPSおよびNGFWソリューションの展開、管理、トラブルシューティングなどのトピックにおける個人の知識とスキルをテストします。
質問 # 187
Refer to the exhibit. An engineer is modifying an access control pokey to add a rule to inspect all DNS traffic that passes through the firewall.
After making the change and deploying the pokey they see that DNS traffic is not bang inspected by the Snort engine. What is the problem?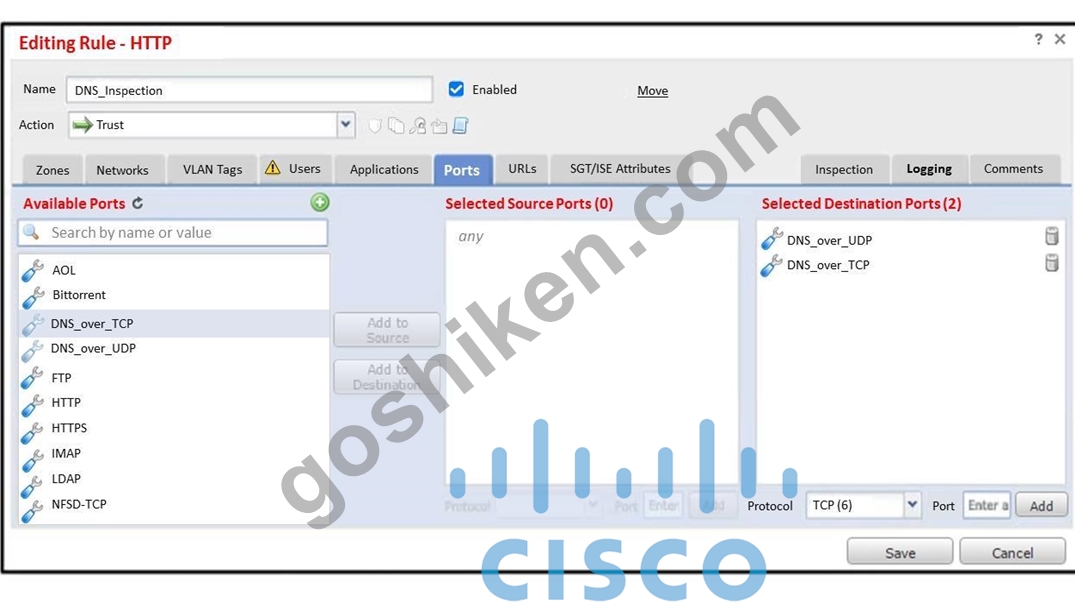
- A. The rule must specify the security zone that originates the traffic
- B. The rule is configured with the wrong setting for the source port
- C. The rule must define the source network for inspection as well as the port
- D. The action of the rule is set to trust instead of allow.
正解:D
質問 # 188
Refer to the exhibit. An engineer is configuring a high-availability solution that has the hardware devices and software versions:
- two Cisco Secure Firewall 9300 Security Appliances with FXOS SW
2.0(1.23)
- one Cisco Secure Firewall Threat Defense with 6.0 1 1 (build 1023)
- one Cisco Secure Firewall Management Center with SW 6 0.1.1 (build
1023)
Which condition must be met to complete the high-availability configuration?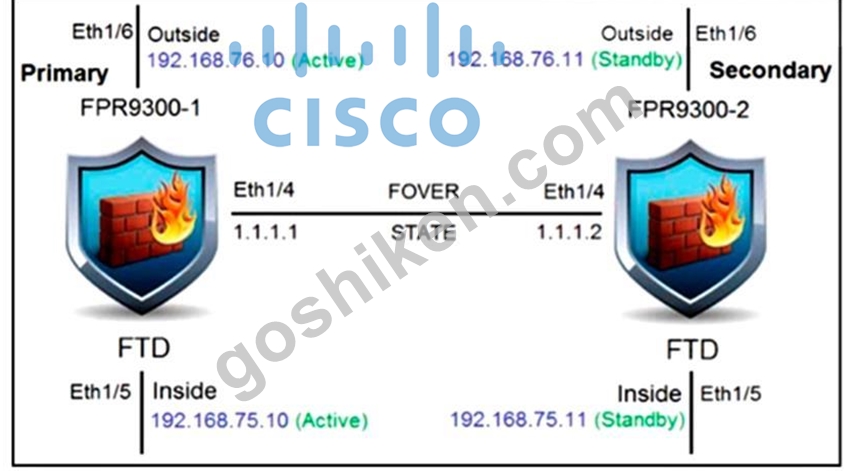
- A. Both firewalls must have the same number of interfaces
- B. The version numbers must have the same patch number
- C. DHCP must be configured on at least one firewall interface.
- D. Both firewalls must be in transparent mode
正解:A
解説:
In a high-availability (HA) setup for Cisco Secure Firewall devices, both firewalls in the HA pair must have identical configurations, which includes having the same number of interfaces with matching names, IP addresses, and settings. This requirement ensures that both devices can function seamlessly as primary and secondary units, allowing for smooth failover without configuration mismatches.
For HA to work properly, each firewall must have the same interface configuration to ensure that both units can handle traffic in the same way when a failover event occurs. If the primary device fails, the secondary device needs to have identical interface configurations to take over immediately.
質問 # 189
Refer to the exhibit.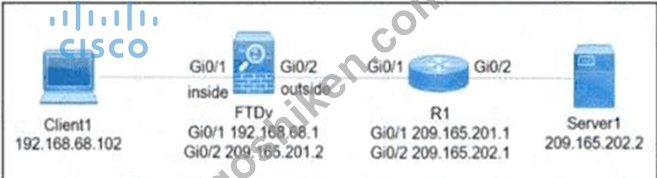
A user on a computer named Client1 is performing a traceroute to IP address 209.165.202.2. Drag and drop the appropriate values onto the fields in the Capture w/Trace configuration and captured-packet output. Not all options are used.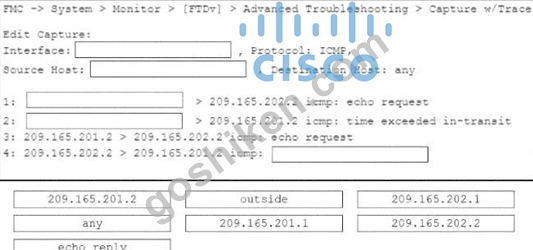
正解:
解説: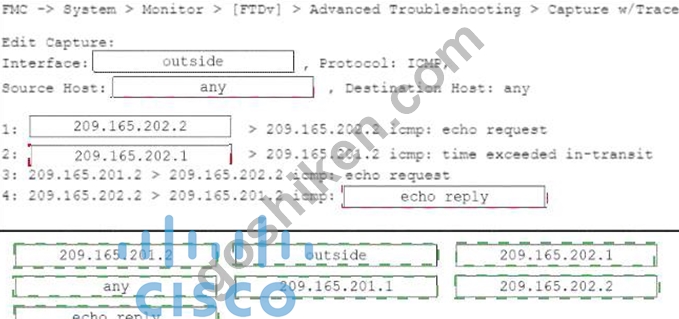
Explanation:
Interface # outside
Source Host # any
Packet 1 source # 209.165.201.2
Packet 2 source # 209.165.201.1
Packet 4 ICMP message # echo reply
Unused Options:
209.165.202.1
209.165.202.2
The capture must run on the FTDv outside interface, where the client's translated address is 209.165.201.2.
Selecting any as the source-host criterion captures both the outbound echo requests and the inbound ICMP responses. The first request therefore appears as 209.165.201.2 to 209.165.202.2. When the initial traceroute probe expires at R1, the router generates an ICMP time-exceeded response using its interface address
209.165.201.1. A later probe reaches Server1, which returns an ICMP echo reply from 209.165.202.2 to
209.165.201.2. The completed-answer exhibit in List B places several IP addresses inconsistently; the mapping above follows the displayed topology and actual ICMP traceroute packet flow. Cisco FTD capture and Packet Tracer guidance
質問 # 190
Refer to the exhibit.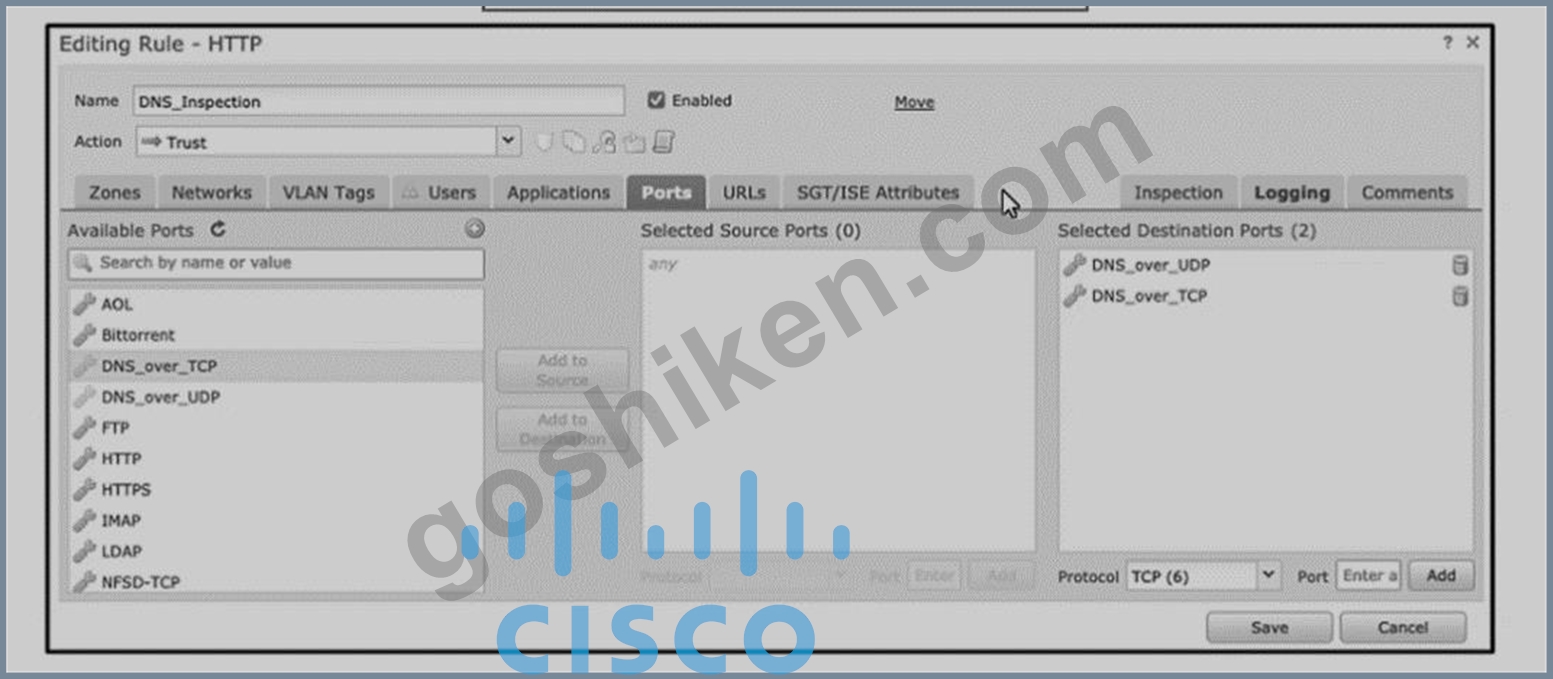
Refer to the exhibit An engineer is modifying an access control pokey to add a rule to inspect all DNS traffic that passes through the firewall After making the change and deploying the pokey they see that DNS traffic is not bang inspected by the Snort engine What is the problem?
- A. The rule must specify the security zone that originates the traffic
- B. The rule is configured with the wrong setting for the source port
- C. The rule must define the source network for inspection as well as the port
- D. The action of the rule is set to trust instead of allow.
正解:D
質問 # 191
A network engineer sets up a secondary Cisco MC that is integrated with Cisco Security Packet Analyzer What occurs when the secondary Cisco MC synchronizes with the primary Cisco FMC?
- A. The secondary Cisco FMC must be reintegrated with the Cisco Security Packet Analyzer after the synchronization
- B. The existing integration configuration is replicated to the primary Cisco FMC
- C. The existing configuration for integration of the secondary Cisco FMC the Cisco Security Packet Analyzer is overwritten.
- D. The synchronization between the primary and secondary Cisco FMC fails
正解:C
質問 # 192
Remote users who connect via Cisco AnyConnect to the corporate network behind a Cisco FTD device report that they get no audio when calling between remote users using their softphones.
These same users can call internal users on the corporate network without any issues. What is the cause of this issue?
- A. FTD has no NAT policy that allows outside to outside communication
- B. The hairpinning feature is not available on FTD.
- C. Split tunneling is enabled for the Remote Access VPN on FTD
- D. The Enable Spoke to Spoke Connectivity through Hub option is not selected on FTD.
正解:A
解説:
For remote users connected via AnyConnect VPN behind a Cisco FTD device, calls between remote users require the FTD to allow traffic between VPN clients, which is considered "outside to outside" traffic since VPN clients are logically on the outside interface.
Without a proper NAT exemption or NAT policy that permits this outside-to-outside communication, the traffic between remote users will be blocked or dropped, causing issues such as no audio during calls.
Cisco FTD requires explicit NAT rules to allow such communication; otherwise, the default behavior blocks this traffic.
https://www.cisco.com/c/en/us/support/docs/security/anyconnect-secure-mobility-client/216180- troubleshoot-common-anyconnect-communica.pdf
質問 # 193
Which two packet captures does the FTD LINA engine support? (Choose two.)
- A. Layer 7 network ID
- B. protocol
- C. source IP
- D. dynamic firewall importing
- E. application ID
正解:B、C
解説:
https://www.cisco.com/c/en/us/support/docs/security/firepower-ngfw/212474-working-with-firepower-threat-defense-f.html
質問 # 194
Refer to the exhibit.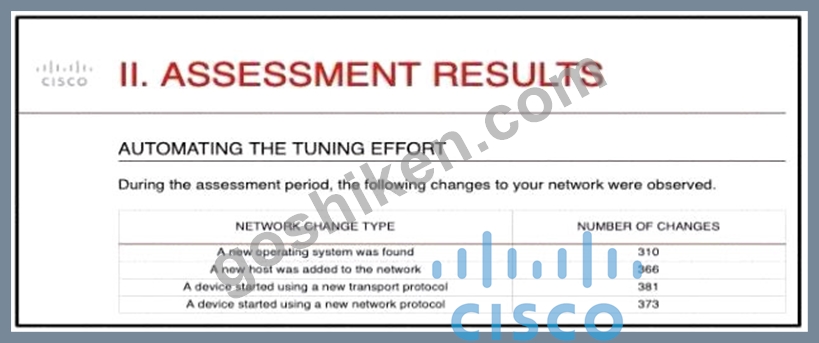
And engineer is analyzing the Attacks Risk Report and finds that there are over 300 instances of new operating systems being seen on the network How is the Firepower configuration updated to protect these new operating systems?
- A. Cisco Firepower gives recommendations to update the policies.
- B. Cisco Firepower automatically updates the policies.
- C. The administrator requests a Remediation Recommendation Report from Cisco Firepower
- D. The administrator manually updates the policies.
正解:A
解説:
Explanation
Ref:
https://www.cisco.com/c/en/us/td/docs/security/firepower/60/configuration/guide/fpmc-config-guide-v60/Tailori
質問 # 195
An engineer wants to perform a packet capture on the Cisco FTD to confirm that the host using IP address 192
168.100.100 has the MAC address of 0042 7734.103 to help troubleshoot a connectivity issue What is the correct tcpdump command syntax to ensure that the MAC address appears in the packet capture output?
- A. -ne src 192.168.100.100
- B. -w capture.pcap -s 1518 host 192.168.100.100 mac
- C. -w capture.pcap -s 1518 host 192.168.100.100 ether
- D. -nm src 192.168.100.100
正解:A
解説:
Reference:
https://www.cisco.com/c/en/us/support/docs/security/firepower-ngfw/212474-working-with-firepower-threat-def
質問 # 196
A network engineer is deploying a Cisco Firepower 4100 appliance and must configure a multi-instance environment for high availability. Drag and drop me actions from the left into sequence on the right far this configuration.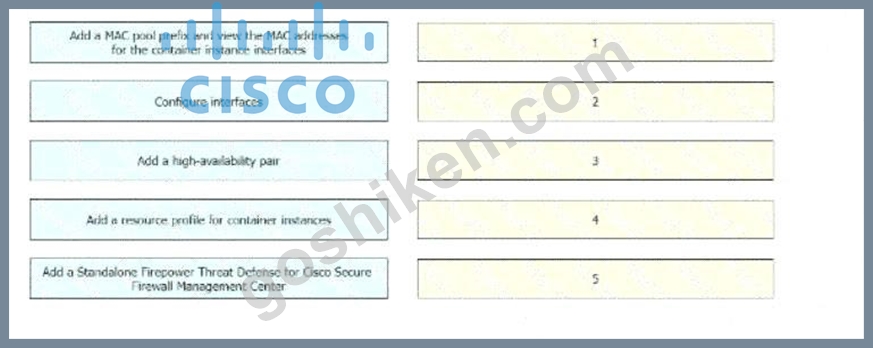
正解:
解説: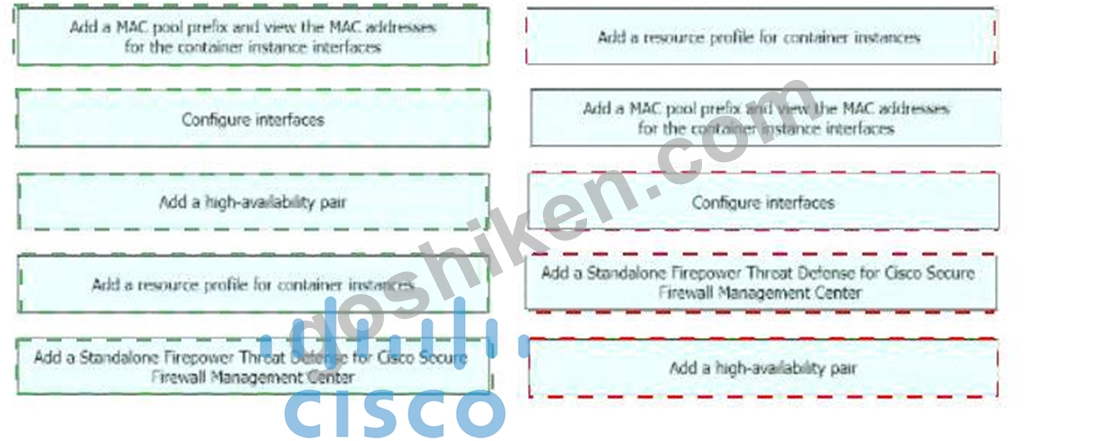
Explanation:
The correct sequence of actions for configuring a multi-instance environment for high availability on a Cisco Firepower 4100 appliance is as follows:
* Add a resource profile for container instances. A resource profile defines the CPU, RAM, and disk space allocation for each container instance.You can create multiple resource profiles with different resource settings and assign them to different container instances1.
* Add a MAC pool prefix and view the MAC address for the container instance interfaces. A MAC pool prefix is a 24-bit prefix that is used to generate MAC addresses for the container instance interfaces.
You can specify a custom MAC pool prefix or use the default one.You can also view the MAC addresses that are assigned to each container instance interface1.
* Configure interfaces. You need to configure the physical interfaces, EtherChannels, and VLAN subinterfaces that will be used by the container instances.You can also configure shared interfaces that can be used by multiple container instances on the same security module/engine1.
* Add a Standalone Firepower Threat Defense for Cisco Secure Firewall Management Center. You need to add a logical device that runs a standalone Firepower ThreatDefense (FTD) application instance and register it with the Cisco Secure Firewall Management Center (FMC).This logical device will act as the management interface for the container instances1.
* Add a high-availability pair. You need to add another logical device that runs a standalone FTD application instance and register it with the FMC as well. Then, you need to configure high availability (HA) between the two standalone FTD logical devices.This will enable HA for the container instances that are associated with them1.
質問 # 197
Within Cisco Firepower Management Center, where does a user add or modify widgets?
- A. dashboard
- B. summary tool
- C. reporting
- D. context explorer
正解:A
解説:
Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/60/configuration/guide/fpmc-config- guide- v60/Using_Dashboards.html
質問 # 198
An engineer currently has a Cisco FTD device registered to the Cisco FMC and is assigned the address of 10 10.50.12. The organization is upgrading the addressing schemes and there is a requirement to convert the addresses to a format that provides an adequate amount of addresses on the network What should the engineer do to ensure that the new addressing takes effect and can be used for the Cisco FTD to Cisco FMC connection?
- A. Cisco FMC does not support devices that use IPv4 IP addresses.
- B. Format and reregister the device to Cisco FMC.
- C. Delete and reregister the device to Cisco FMC
- D. Update the IP addresses from IPV4 to IPv6 without deleting the device from Cisco FMC
正解:D
質問 # 199
An engineer is attempting to create a new dashboard within the Cisco FMC to have a single view with widgets from many of the other dashboards. The goal is to have a mixture of threat and security related widgets along with Cisco Firepower device health information. Which two widgets must be configured to provide this information? (Choose two.)
- A. Network Compliance
- B. Appliance Status
- C. Correlation Information
- D. Intrusion Events
- E. Current Sessions
正解:B、D
解説:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/640/configuration/guide/fpmc-config-guide-v64/ dashboards.html#ID-2206-00000283
質問 # 200
A network engineer is configuring URL Filtering on Firepower Threat Defense. Which two port requirements on the Firepower Management Center must be validated to allow communication with the cloud service? (Choose two.)
- A. inbound port TCP/80
- B. outbound port TCP/443
- C. outbound port TCP/80
- D. outbound port TCP/8080
- E. inbound port TCP/443
正解:B、C
解説:
Section: Management and Troubleshooting
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/60/configuration/guide/fpmc-config-guide- v60/Security__Internet_Access__and_Communication_Ports.html
質問 # 201
An engineer must define a URL object on Cisco FMC.
What is the correct method to specify the URL without performing SSL inspection?
- A. Specify all subdomains in the object group.
- B. Include all URLs from CRL Distribution Points.
- C. Use Subject Common Name value.
- D. Specify the protocol in the object.
正解:C
解説:
HTTPS filtering, unlike HTTP filtering, disregards subdomains within the subject common name.
Do not include subdomain information when manually filtering HTTPS URLs.
https://www.cisco.com/c/en/us/td/docs/security/firepower/670/fdm/fptd-fdm-config-guide-670/fptd-fdm-access.html
質問 # 202
Which Cisco Firepower feature is used to reduce the number of events received in a period of time?
- A. thresholding
- B. rate-limiting
- C. correlation
- D. suspending
正解:A
質問 # 203
A mid-sized company is experiencing higher network bandwidth utilization due to a recent acquisition The network operations team is asked to scale up their one Cisco FTD appliance deployment to higher capacities due to the increased network bandwidth. Which design option should be used to accomplish this goal?
- A. Deploy multiple Cisco FTD HA pairs to increase performance
- B. Deploy multiple Cisco FTD appliances in firewall clustering mode to increase performance.
- C. Deploy multiple Cisco FTD appliances using VPN load-balancing to scale performance.
- D. Deploy multiple Cisco FTD HA pairs in clustering mode to increase performance
正解:B
解説:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/fxos/clustering/ftd-cluster-solution.html#concept_C8502505F840451C9E600F1EED9BC18E
質問 # 204
Refer to the exhibit.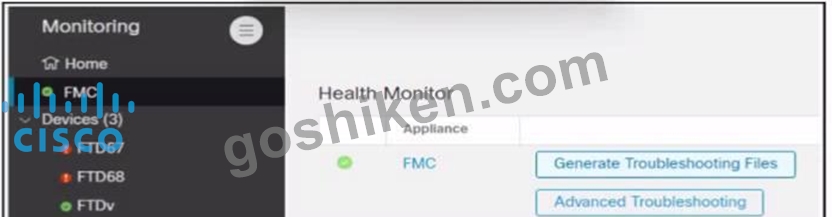
An engineer generates troubleshooting files in Cisco Secure Firewall Management Center (FMC). A successfully completed task Is removed before the files are downloaded. Which two actions must be taken to determine the filename and obtain the generated troubleshooting files without regenerating them? (Choose two.)
- A. Connect to CU on the FTD67 and FTD66 devices and copy the tiles from flash to the PIP server.
- B. Use an FTP client Hi expert mode on Secure FMC lo upload the files to the FTP server.
- C. Go to expert mode on Secure FMC. list the contents of/Var/common, and determine the correct filename from the output
- D. Click System Monitoring, men Audit to determine the correct filename from the line containing the Generate Troubleshooting Files string.
- E. Go to the same screen as shown in the exhibit, click Advanced Troubleshooting, enter the rile name, and then start the download
正解:C、D
解説:
If a task to generate troubleshooting files in Cisco Secure Firewall Management Center (FMC) is completed successfully but removed before the files are downloaded, the following steps can be taken to determine the filename and obtain the generated troubleshooting files without regenerating them:
* Go to expert mode on Secure FMC:
* Access expert mode on the FMC via SSH or the console.
* List the contents of the directory /var/common to locate the generated troubleshooting files. Use the command ls /var/common.
* Use the System Monitoring Audit logs:
* In FMC, navigate to System > Monitoring > Audit.
* Find the line containing the "Generate Troubleshooting Files" string to determine the correct filename.
These actions help identify and retrieve the generated troubleshooting files without the need to regenerate them, saving time and resources.
References: Cisco Secure Firewall Management Center Administrator Guide, Chapter on Troubleshooting and File Management.
質問 # 205
An engineer is deploying a Cisco Secure Firewall Management Center appliance. The company must send data to Cisco Secure Network Analytics appliances. Which two actions must the engineer take? (Choose two.)
- A. Add the Netflow_Set_Parameters object to the configuration.
- B. Add the Netflow_Send_Destination object to the configuration.
- C. Security Intelligence object to send data to Cisco Secure Network Analytics
- D. Add the Netflow_Add_Destination object to the configuration.
- E. Create a service identifier to enable the NetFlow service.
正解:A、D
質問 # 206
A network administrator reviews the file report for the last month and notices that all file types, except exe.
show a disposition of unknown. What is the cause of this issue?
- A. A file policy has not been applied to the access policy.
- B. The malware license has not been applied to the Cisco FTD.
- C. The Cisco FMC cannot reach the Internet to analyze files.
- D. Only Spero file analysis is enabled.
正解:A
解説:
Explanation
A file policy defines the actions that the Cisco Firepower Threat Defense (FTD) device should take when it encounters different types of files. The file policy is applied as part of an access control policy. If an access control policy does not include a file policy, the FTD device will not take any action on the files it encounters, resulting in a disposition of "unknown" for all file types except exe.
Reference:
https://www.cisco.com/c/en/us/support/docs/security/firepower-ngfw/219759-configure-bypass-policies-on-the-c
質問 # 207
An engineer is troubleshooting application failures through a FTD deployment.
While using the FMC CLI. it has been determined that the traffic in question is not matching the desired policy. What should be done to correct this?
- A. Use the system support network-options command to fine tune the policy.
- B. Use the system support application-identification-debug command to determine which rules the traffic matching and modify the rule accordingly
- C. Use the system support firewall-engine-debug command to determine which rules the traffic matching and modify the rule accordingly
- D. Use the system support firewall-engine-dump-user-f density-data command to change the policy and allow the application through the firewall.
正解:C
質問 # 208
Refer to the exhibit.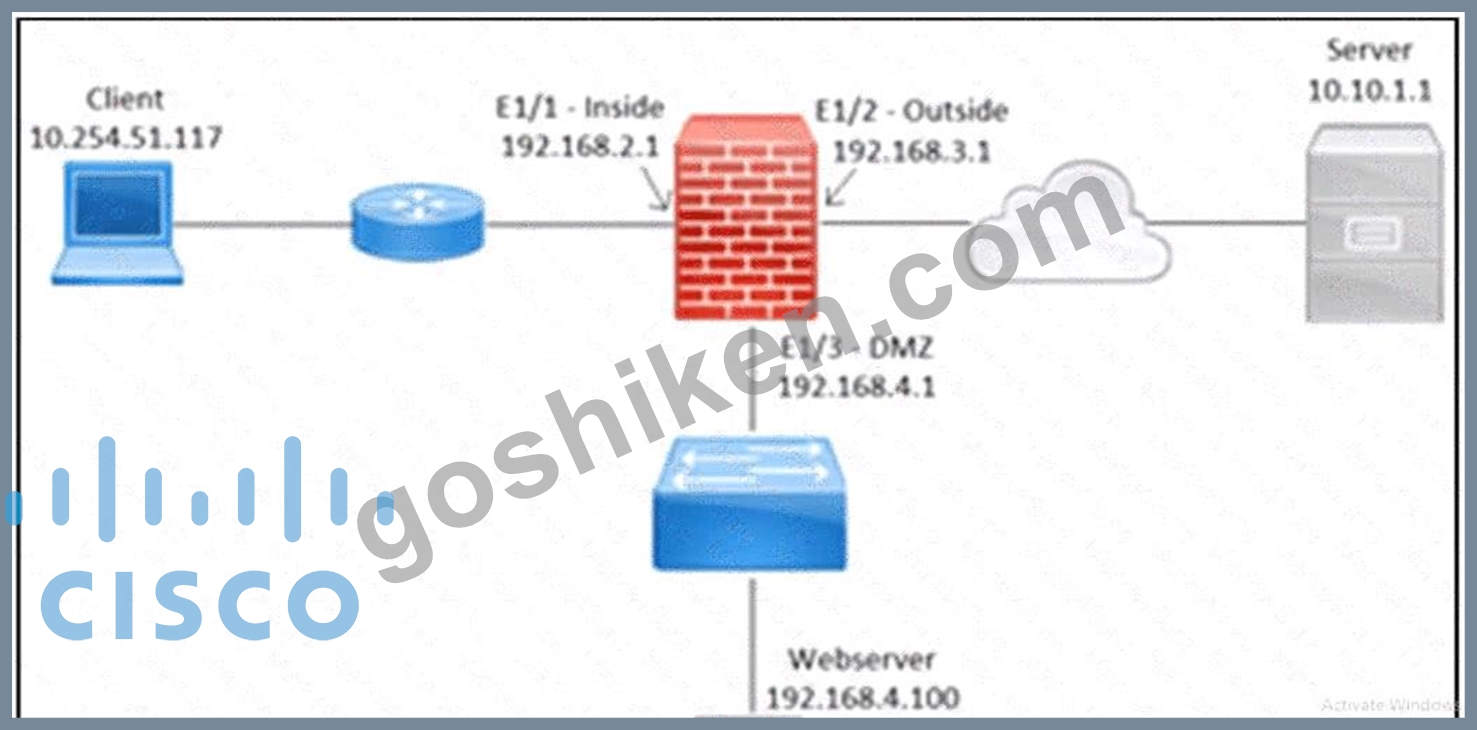
A client with IP address 10.254.51.117 connects through a Cisco Secure Firewall Threat Defense device toward a website at 10.10.1.1. The packet capture shows repeated TCP SYN packets from the client without completion of the three-way handshake. Which action must the engineer take to resolve the issue?
- A. Add a firewall rule that allows ACK responses from the inside to the outside.
- B. Configure the outside interface to receive SYN-ACK messages.
- C. Configure the inside interface to send ACK messages.
- D. Add a firewall rule that allows the web server to communicate with the DMZ.
正解:B
解説:
The capture shows that the client repeatedly transmits a TCP SYN but does not receive the SYN-ACK required to advance the connection state. This indicates that the return portion of the TCP three-way handshake is not reaching the expected ingress interface or is not being processed there. The outside interface must therefore be configured or connected so that the returning SYN-ACK packets arrive through the interface where the firewall expects them. An access rule does not instruct an interface to generate TCP acknowledgement messages; ACK and SYN-ACK packets are produced by the communicating endpoints.
Likewise, permitting communication "with the DMZ" does not address the missing return-handshake packet shown in the capture. Correcting the return path through the outside interface allows the firewall to observe both directions, establish state, and forward the subsequent packets.
質問 # 209
An engineer wants to add an additional Cisco FTD Version 6.2.3 device to their current 6.2.3 deployment to create a high availability pair. The currently deployed Cisco FTD device is using local management and identical hardware including the available port density to enable the failover and stateful links required in a proper high availability deployment. Which action ensures that the environment is ready to pair the new Cisco FTD with the old one?
- A. Ensure that the two devices are assigned IP addresses from the 169 254.0.0/16 range for failover interfaces.
- B. Change from Cisco FDM management to Cisco FMC management on both devices and register them to FMC.
- C. Ensure that the configured DNS servers match on the two devices for name resolution.
- D. Factory reset the current Cisco FTD so that it can synchronize configurations with the new Cisco FTD device.
正解:B
質問 # 210
An engineer is tasked with deploying an internal perimeter firewall that will support multiple DMZs Each DMZ has a unique private IP subnet range. How is this requirement satisfied?
- A. Deploy the firewall in routed mode with NAT configured.
- B. Deploy the firewall in transparent mode with NAT configured.
- C. Deploy the firewall in transparent mode with access control policies.
- D. Deploy the firewall in routed mode with access control policies.
正解:D
質問 # 211
......
あなたを合格させるCCNP Security 300-710試験問題集で2026年08月27日には423問あります:https://www.goshiken.com/Cisco/300-710-mondaishu.html
最新のCisco 300-710のPDFと問題集で(2026)無料試験問題解答:https://drive.google.com/open?id=15XI7BcpW__tKxq0MMnukZVbXlsSVZ7MY