
一番最新のCyberArk CPC-CDE-RECERT試験問題集PDFには2026年更新
100%無料CyberArk Certification CPC-CDE-RECERT問題集PDFお試しサンプル認定ガイドがカバーされます
質問 # 15
Which statements accurately describe the process of LDAP integration with CyberArk Privilege Cloud Standard? (Choose two.)
- A. A tailored Python script is required to facilitate the LDAP server interaction.
- B. The LDAP BIND user requires domain administrative privileges for a successful connection.
- C. Directory maps determine user or group creation within the Privilege Cloud Vault.
- D. Upon user login, their directory attributes are refreshed through the directory map.
- E. For establishing a connection, the domain base context is not a prerequisite.
正解:C、D
解説:
* CyberArk states that LDAP users are provisioned using directory maps, and that a directory map determines whether a user account or group may be created in Privilege Cloud (and under which criteria/templates). That's A.
* CyberArk also states that an LDAP user's account properties are updated by the directory map each time the user logs on (i.e., attributes refresh on login). That's C.
Why the others are incorrect:
* B: No custom Python script is required-Privilege Cloud uses built-in LDAP integration/directory mapping.
* D: A Base Context / search base (e.g., DC=example,DC=com) is part of the required LDAP connection configuration.
* E: The bind user does not have to be a domain admin; typical LDAP bind accounts are least-privileged for directory reads (domain admin is not a prerequisite in CyberArk's integration flow).
質問 # 16
When installing PSM on a Windows 2019 Server, under which circumstances should the PSMConnect and PSMAdminConnect users be moved to the domain? (Choose two.)
- A. When you need to enable PSM for Web Support
- B. When RDS CAL Per User licenses are in use
- C. When you want to load balance the PSM installation
- D. When the RDS session broker has a value > 1
- E. When you want to extend PSM sessions beyond one hour
正解:B、E
解説:
CyberArk explicitly states that you must move PSM application users (PSMConnect/PSMAdminConnect) to domain users on Windows 2019/2022 when:
* you are using RDS CAL per-user licensing, and
* you want to extend PSM sessions beyond one hour.
質問 # 17
Which option correctly describes the authentication differences between CyberArk Privilege Cloud and CyberArk PAM Self-Hosted?
- A. CyberArk Privilege Cloud only provides a username and password authentication without third-party IdP integration; CyberArk PAM Self-Hosted uses traditional on-premises methods such as Windows and LDAP. but lacks modern protocols such as SAML or OIDC.
- B. Both use the same authentication methods.
- C. CyberArk Privilege Cloud requires on-premises components for all authentication and does not support other cloud-based authentication protocols; CyberArk PAM Self-Hosted offers a wide array of methods, including support for SAML. OIDC. and other modern protocols, without needing on- premises components.
- D. CyberArk Privilege Cloud uses cloud-based methods, integrating with CyberArk Identity for MFA. and supports SAML and OIDC; CyberArk PAM Self-Hosted depends on on-premises methods such as RADIUS and LDAP, but can adopt SAML or OIDC with additional setups.
正解:D
解説:
The correct description of the authentication differences between CyberArk Privilege Cloud and CyberArk PAM Self-Hosted is that CyberArk Privilege Cloud uses cloud-based methods, integrating with CyberArk Identity for Multi-Factor Authentication (MFA), and supports SAML and OIDC, while CyberArk PAM Self- Hosted relies on on-premises methods such as RADIUS and LDAP, but can adopt SAML or OIDC with additional setups. CyberArk Privilege Cloud is designed to leverage modern cloud-based authentication protocols to enhance security and ease of use, particularly in distributed and diverse IT environments. In contrast, CyberArk PAM Self-Hosted offers flexibility to use traditional on-premises authentication methods but also supports modern protocols if configured to do so.
質問 # 18
The System Health page shows the status of all components related to Privilege Cloud. Which components can administrators monitor on this page? (Choose two.)
- A. PVWA
- B. PTA
- C. Vault
- D. PSM
- E. CPM
正解:D、E
解説:
In Privilege Cloud Shared Services, the System Health dashboard lists component categories that include CPM (and Accounts Discovery) and PSM (and PSM for SSH), along with Web Portal and Secrets Manager Credential Providers. Vault/PVWA/PTA are not listed as monitorable components on this page in the Privilege Cloud Shared Services System Health topic.
質問 # 19
Which statements are correct regarding enabling end users from multiple domains in the same forest to authenticate to CyberArk Privilege Cloud? (Choose two.)
- A. Configuring authentication for users in multiple domains in the same forest is not recommended due to potential performance issues.
- B. This can be accomplished when the users' Active Directory accounts are in domains with domain controllers that have a two-way, transitive trust relationship with the domain controller to which the connector is connected.
- C. CyberArk recommends consolidating users from multiple domains in the same forest into the CyberArk Cloud Directory for this specific use case.
- D. To enable authentication for users in multiple domains in the same forest, you should install separate CyberArk Identity Connectors for each independent domain.
- E. CyberArk does not permit end users from multiple domains to authenticate to CyberArk Privilege Cloud; it only allows users from multiple directory services, such as AD, Azure AD, CyberArk Cloud Directory, etc.
正解:B、D
解説:
CyberArk's official connector guidance (CyberArk Identity / Identity Administration-used with Privilege Cloud Shared Services for AD user authentication) says that for trusted domains in a single forest, you use this model when the domain controllers have a two-way, transitive trust relationship with the domain controller the connector is joined to.
It also clarifies that a single connector can be used for the entire domain tree or forest in that trusted- domain model, and authentication requests are handled according to AD trust relationships within the forest
/tree.
https://docs.cyberark.com/identity/latest/en/content/coreservices/connector/userauthmultdomain.htm
質問 # 20
Which users are Privilege Cloud Standard built-in users? (Choose 2.)
- A. remoteAccessAppUser
- B. NASCorp
- C. CyberArkAdmin
- D. PASReporterUser
- E. saascorps
正解:A、E
解説:
https://docs.cyberark.com/privilege-cloud-standard/latest/en/content/privilege%20cloud/privcloud-app-users.
htm
質問 # 21
CyberArk User Neil is trying to connect to the Target Linux server 192.168.1.164 using a domain user ACME\linuxuser01 on domain acme.corp using PSM for SSH server
192.168.65.145.
What is the correct syntax?
- A. ssh neil@[email protected]@[email protected]
- B. ssh neil@linuxuser01:[email protected]@192.168.65.145
- C. ssh neil@linuxuser01#[email protected]@192.168.65.145
- D. sshneil@[email protected]@192.168.65.145
正解:C
解説:
In CyberArk Privilege Cloud, when connecting to a target server using the Privileged Session Manager (PSM) for SSH, the correct syntax for the SSH command includes the following format: ssh neil@linuxuser01#[email protected]@192.168.65.145. This syntax breaks down as follows:
* neil: The CyberArk username.
* linuxuser01#acme.corp: The domain user on the target Linux server, formatted as username#domain.
* 192.168.1.164: The IP address of the target Linux server.
* 192.168.65.145: The IP address of the PSM for SSH server.
This specific format ensures that the CyberArk Privileged Access Manager correctly interprets and routes the connection through the PSM for SSH to the intended target server.
:
CyberArk Privilege Cloud Introduction
CyberArk Privileged Access Manager
CyberArk Privilege Cloud - Manage Safe Members
CyberArk Security Fundamentals
質問 # 22
Arrange the steps to failover to the passive CPM in the correct sequence.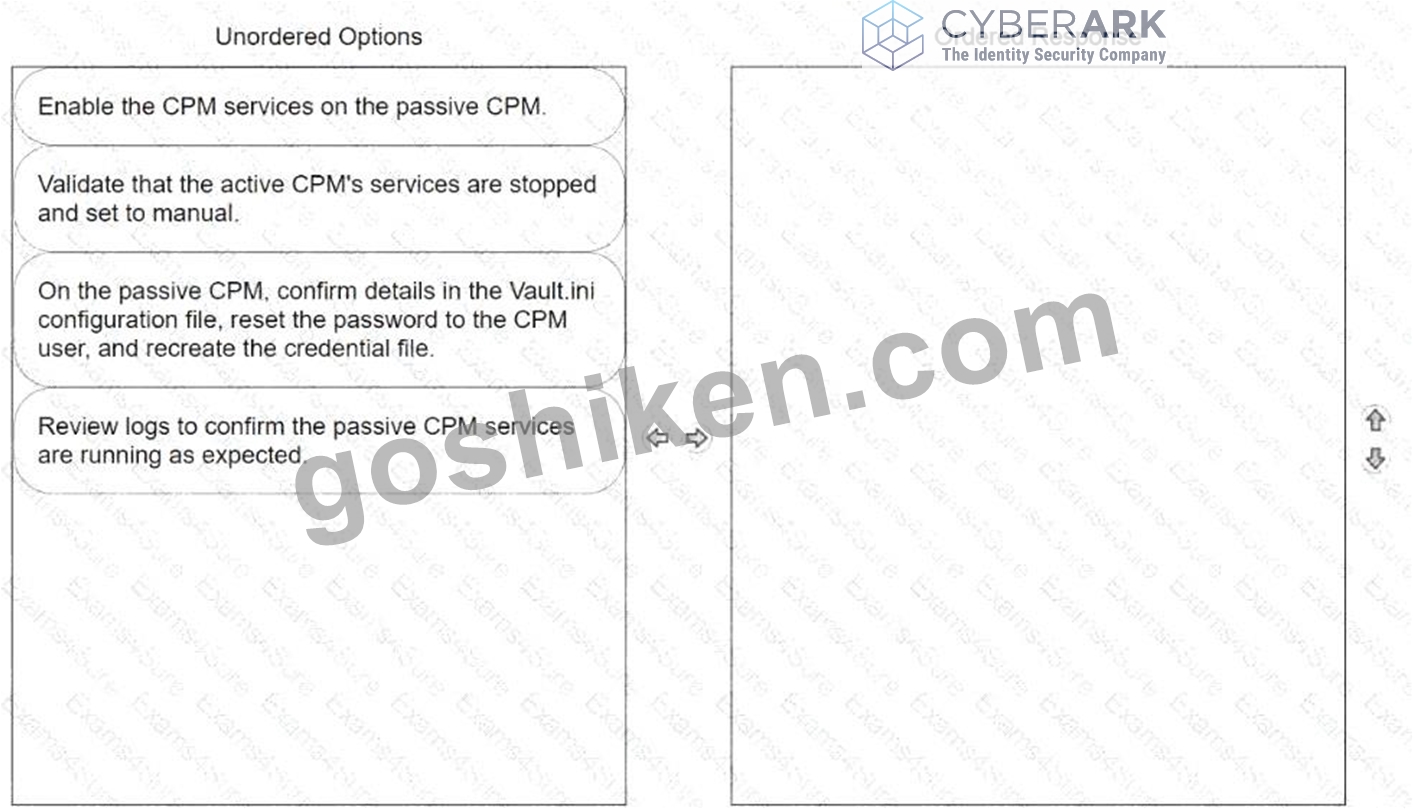
正解:
解説: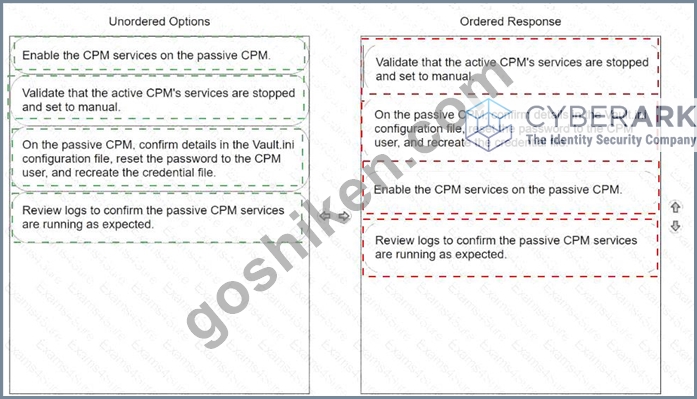
Explanation:
To properly arrange the steps for failing over to a passive Central Policy Manager (CPM) in CyberArk, the sequence should be as follows:
* Validate that the active CPM's services are stopped and set to manual.Before enabling the passive CPM, ensure that the services on the active CPM are stopped. This prevents any conflicts or data corruption by making sure that only one CPM is active at a time. Setting the services to manual ensures they do not restart automatically, which is crucial during a failover scenario.
* On the passive CPM, confirm details in the Vault.ini configuration file, reset the password to the CPM user, and recreate the credential file.This step involves making sure the passive CPM has the correct configuration to seamlessly take over operations. Adjustments in the Vault.ini file may be necessary to ensure it is pointing to the correct Vault and network settings. Resetting the password and recreating the credential file are critical to secure the login and authentication process for the newly active CPM.
* Enable the CPM services on the passive CPM.Once the passive CPM is correctly configured and ready, enable its services to begin handling the tasks and responsibilities of the primary CPM. This action effectively switches the role from passive to active, enabling the passive CPM to function as the new operational manager.
* Review logs to confirm the passive CPM services are running as expected.Finally, review the system and application logs to confirm that the now-active CPM is operating correctly and that all services have started without errors. This step is vital for verifying that the failover process was successful and that the system is stable.
Following this ordered sequence ensures a smooth transition of roles from the active CPM to the passive CPM, minimizing downtime and potential disruptions in the privileged access management operations.
質問 # 23
A support team has asked you to provide the previous password for an account that had its password recently changed by the CPM. In which tab within the account's overview page can you retrieve this information?
- A. Versions
- B. Overview
- C. Activities
- D. Details
正解:A
解説:
To retrieve the previous password for an account that had its password changed by the CPM, you should look under the Versions tab within the account's overview page. This tab maintains a history of password changes, including previous passwords, along with other historical data points that allow for tracking changes over time. This feature is critical for auditing and rollback purposes in environments where knowing past credentials is necessary for troubleshooting or compliance.
質問 # 24
You plan to install Privilege Cloud Connectors on your AWS and Azure environments.
What is the maximum number of concurrent RDP/SSH sessions that each connector can handle for Large Implementations?
- A. 0
- B. 31-60
- C. 1
- D. 1-10
正解:B
解説:
For large implementations of CyberArk Privilege Cloud Connectors in AWS and Azure environments, each connector can handle between 31-60 concurrent RDP/SSH sessions. This capacity is specified in the CyberArk documentation concerning Privilege Cloud Connectors and their scalability options. It is designed to support a higher volume of concurrent sessions to meet the needs of larger enterprise environments, ensuring that multiple users can securely access resources without significant performance degradation.
質問 # 25
Arrange the steps to install a passive CPM using the Privilege Cloud installer in the correct sequence.
正解:
解説:
Explanation:
4->1->2->3
https://docs.cyberark.com/privilege-cloud-standard/latest/en/content/privilege%20cloud/privcloud-cpm-dr- install-standard.htm
質問 # 26
In large-scale environments, it is important to enable the CPM to focus its search operations on specific Safes instead of scanning all Safes it sees in the Vault. How is this accomplished?
- A. Administration Options > CPM Settings
- B. AllowedSafes Parameter on each platform policy
- C. Administration > Options > CPM Scanner.
- D. MaxConcurrentConnection parameter on each platform policy
正解:B
解説:
In large-scale environments, to enable the Central Policy Manager (CPM) to focus its search operations on specific Safes instead of scanning all Safes it sees in the Vault, the AllowedSafes parameter on each platform policy is used. This parameter can be configured within the platform settings in the CyberArk administration interface. By specifying safes in the AllowedSafes parameter, the CPM will only manage credentials within those designated safes, thereby optimizing performance and managing resources more efficiently by not scanning unnecessary safes. This setting is crucial for large environments where the CPM needs to be as efficient as possible due to the volume of managed accounts.
質問 # 27
Your customer is using Privilege Cloud Shared Services. What is the correct CyberArk Vault address for this customer?
- A. vault-<subdomain>.privilegecloud.cyberark.cloud
- B. v-<subdomain>.privilegecloud.cyberark.cloud
- C. carkvault-<subdomain>.privilegecloud.cyberark.cloud
- D. carkvlt-<subdomain> privilegecloud.cyberark.cloud
正解:A
解説:
For customers using CyberArk Privilege Cloud Shared Services, the correct format for the CyberArk Vault address is:
* vault-<subdomain>.privilegecloud.cyberark.cloud (Option B). This format is used to access the vault services provided by CyberArk in the cloud environment, where <subdomain> is the unique identifier assigned to the customer's specific instance of the Privilege Cloud.
Reference: CyberArk's Privilege Cloud documentation provides details on how to access various services, including the vault. The standard naming convention for accessing the vault services in the cloud typically follows this format.
質問 # 28
Your customer recently merged with a smaller organization. The customer's connector has no network connectivity to the smaller organization's infrastructure. You need to map LDAP users from both your customer and the smaller organization. How is this achieved?
- A. Deploy Identity Connectors in the newly acquired infrastructure and create user mappings.
- B. Switch all users to SAML authentication as there can only be one Identity Connector.
- C. Create the required users in one directory and configure the Identity Connector to read that directory, as there can only be one Identity Connector.
- D. Create mappings for both directories from the original Identity Connector.
正解:A
解説:
To map LDAP users from both your customer and the smaller organization they have merged with, especially when there is no network connectivity between the two infrastructures, the best approach is to:
* Deploy Identity Connectors in the newly acquired infrastructure and create user mappings (Option C). This involves setting up additional Identity Connectors within the smaller organization's network. These connectors will facilitate the integration of user directories from both organizations into the customer's Privilege Cloud environment.
Reference: CyberArk documentation on Identity Connectors often outlines the capability of deploying multiple connectors to manage different user directories, especially useful in scenarios involving mergers or acquisitions where separate infrastructures need integration.
質問 # 29
What is a supported certificate format for retrieving the LDAPS certificate when not using the Cyberark provided LDAPS certificate tool?
- A. p7c
- B. .der
- C. p12
- D. .p7b
正解:B
解説:
For retrieving the LDAPS certificate when not using the CyberArk provided LDAPS certificate tool, the supported certificate format is .der. The DER (Distinguished Encoding Rules) format is a binary form of a certificate rather than the ASCII PEM format. This format is widely supported across various systems for securing LDAP connections by providing a mechanism for LDAP servers to authenticate themselves to users.
This information can be verified by checking LDAP configuration guides and CyberArk's secure implementation documentation which outline supported certificate formats for LDAP integrations.
質問 # 30
Which Safe(s) does the AllowedSafes=Win platform parameter configuration match? (Choose two.)
- A. SQL-Win-SA
- B. WiNdOwS_Accts
- C. win-ssh-keys
- D. WindowsPasswords
- E. CXD-WIN-ADMINS
正解:A、D
解説:
AllowedSafes is a regular expression and is case sensitive.
The regex Win (with no anchors) will match any Safe name that contains the exact substring "Win" with the same case:
* WindowsPasswords # starts with Win #
* SQL-Win-SA # contains Win #
* win-ssh-keys # contains win (lowercase) # (case sensitive)
* CXD-WIN-ADMINS # contains WIN (all caps) #
* WiNdOwS_Accts # mixed case, does not contain the exact substring Win # Therefore the correct choices are A and D.
質問 # 31
Before the hardening process, your customer identified a PSM Universal Connector executable that will be required to run on the PSM. Which file should you update to allow this to run?
- A. PSMAppConfig.xml
- B. PSMHardening.xml
- C. PSMConfigureHardening xml
- D. PSMConfigureAppLocker.xml
正解:D
解説:
To allow a PSM Universal Connector executable to run on the PSM after the hardening process, you should update the PSMConfigureAppLocker.xml file. This file configures AppLocker, which is a feature that controls which apps and files users can run on a system. Including the necessary executable in the PSMConfigureAppLocker.xml ensures it is whitelisted by AppLocker policies, thus permitted to execute even under the hardened security settings of the PSM environment. References to this configuration can be found in the CyberArk Privilege Session Manager implementation documentation, specifically in sections detailing customization and security hardening of environment configurations.
質問 # 32
What is recommended when applying GPO (Group Policy Object) hardening for in-domain PSM servers?
- A. Apply the GPO provided by CyberArk onto the servers after other GPOs.
- B. Place the servers which have PSM installed into a dedicated organizational unit (OU).
- C. After installation, remove the PSM servers from the domain to maximize security.
- D. Apply the GPO hardening to all hosts that end-users will connect to through the PSM.
正解:B
解説:
CyberArk's PSM hardening procedure for In Domain deployments explicitly recommends linking the hardening GPO to a dedicated OU and ensuring the CyberArk servers are located under that OU so the hardening GPO does not affect any other server.
This directly matches D.
質問 # 33
......
更新されたのはCyberArk CPC-CDE-RECERT問題集PDFオンラインエンジン:https://www.goshiken.com/CyberArk/CPC-CDE-RECERT-mondaishu.html
PDF試験材料は2026年最新の実際に出るCPC-CDE-RECERT問題集:https://drive.google.com/open?id=1D-9Aj2n8j7JVuH2-1eknrtQqfwh9Ol17