

[2024年06月] 更新されたのはFortinet NSE7_SDW-7.0問題集PDFオンラインエンジン
NSE7_SDW-7.0.PDFで問題解答PDFサンプル問題は信頼され続ける
質問 # 28
Refer to the exhibit, which shows the IPsec phase 1 configuration of a spoke.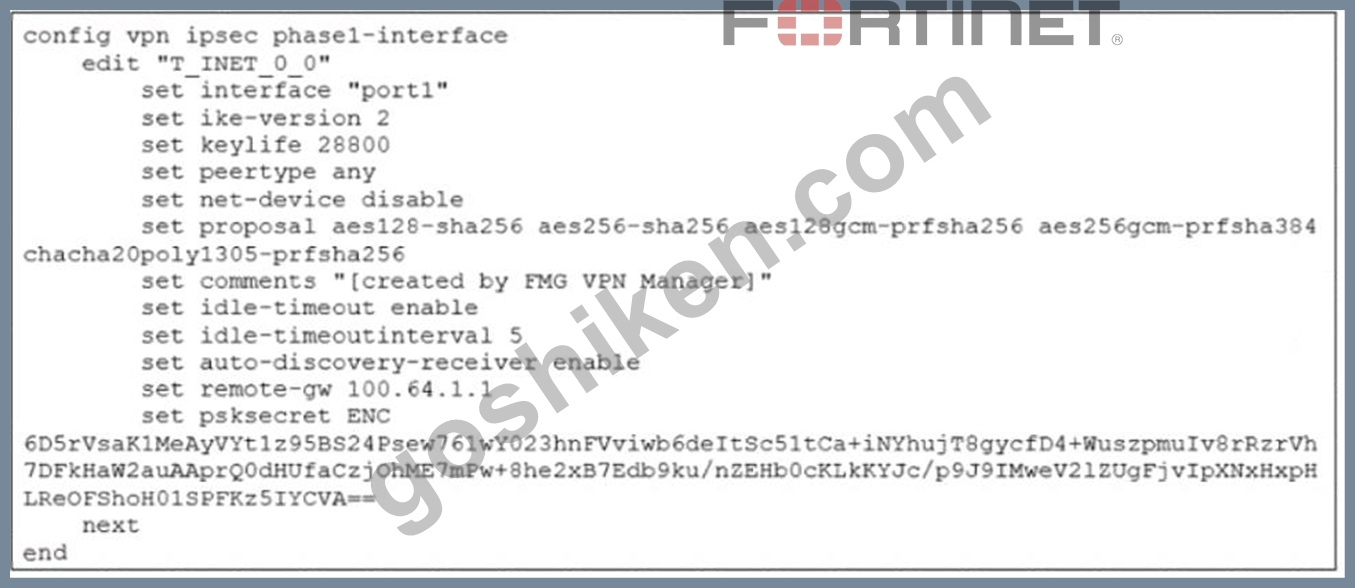
What must you configure on the IPsec phase 1 configuration for ADVPN to work with SD-WAN?
- A. You must set ike-version to 1.
- B. You must enable auto-discovery-sender.
- C. You must disable idle-timeout.
- D. You must enable net-device.
正解:D
質問 # 29
Refer to the exhibits.
Exhibit A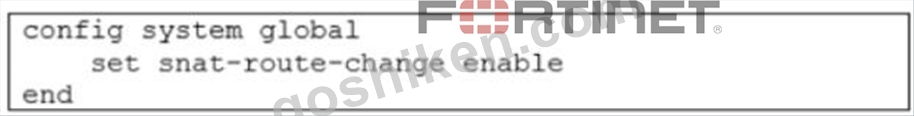
Exhibit B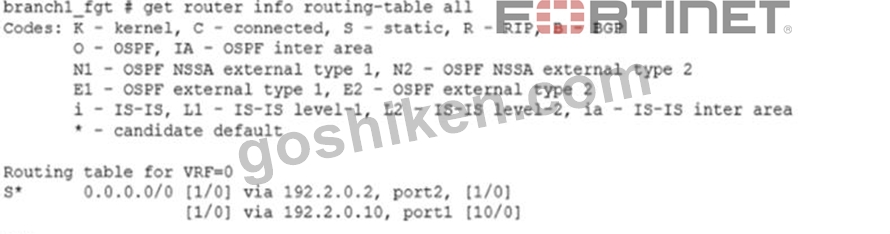
Exhibit A shows the source NAT (SNAT) global setting and exhibit B shows the routing table on FortiGate.
Based on the exhibits, which two actions does FortiGate perform on existing sessions established over port2, if the administrator increases the static route priority on port2 to 20? (Choose two.)
- A. FortiGate updates the gateway information of the sessions with SNAT so that they use port1 instead of port2.
- B. FortiGate continues routing the sessions with no SNAT, over port2.
- C. FortiGate flags the sessions as dirty.
- D. FortiGate performs a route lookup for the original traffic only.
正解:A、C
質問 # 30
Refer to the exhibit.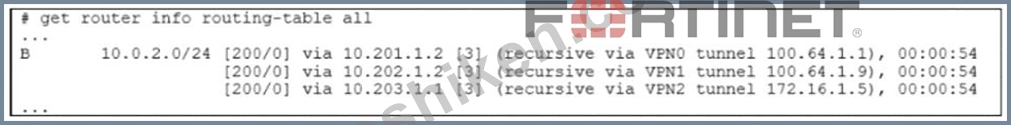
The device exchanges routes using IBGP.
Which two statements are correct about the IBGP configuration and routing information on the device?
(Choose two.)
- A. ibgp-multipath is disabled.
- B. You can run the get router info routing-table database command to display the additional paths.
- C. Each BGP route is three hops away from the destination.
- D. additional-path is enabled.
正解:B、D
質問 # 31
Refer to the exhibit.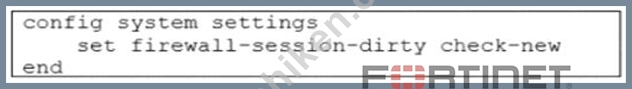
Based on the exhibit, which two actions does FortiGate perform on sessions after a firewall policy change?
(Choose two.)
- A. FortiGate flushes all sessions.
- B. FortiGate does not change existing sessions.
- C. FortiGate evaluates new sessions.
- D. FortiGate terminates the old sessions.
正解:B、C
解説:
Explanation
FortiGate not to flag existing impacted session as dirty by setting firewall-session-dirty to check new. The results is that FortiGate evaluates only new session against the new firewall policy.
質問 # 32
Which two tasks are part of using central VPN management? (Choose two.)
- A. FortiManager installs VPN settings on both managed and external gateways.
- B. You can configure full mesh, star, and dial-up VPN topologies.
- C. You must enable VPN zones for SD-WAN deployments.
- D. You configure VPN communities to define common IPsec settings shared by all VPN gateways.
正解:B、D
質問 # 33
Which two statements about SLA targets and SD-WAN rules are true? (Choose two.)
- A. Member metrics are measured only if an SLA target is configured.
- B. SLA targets are used only by SD-WAN rules that are configured with Lowest Cost (SLA) or Maximize Bandwidth (SLA) as strategy.
- C. SD-WAN rules use SLA targets to check if the preferred members meet the SLA requirements.
- D. When configuring an SD-WAN rule, you can select multiple SLA targets of the same performance SLA.
正解:B、C
質問 # 34
Which CLI command do you use to perform real-time troubleshooting for ADVPN negotiation?
- A. get ipsec tunnel list
- B. diagnose debug application ike
- C. get router info routing-table all
- D. diagnose vpn tunnel list
正解:B
解説:
IKE real-time debug - useful when debugging ADVPN shortcut messages and spoke-to-spoke negotiations.
* diagnose debug console timestamp enable
* diagnose vpn ike log filter clear
* diagnose vpn ike log filter mdst-addr4 <ip.of.hub> <ip.of.spoke>
* diagnose debug application ike -1
* diagnose debug enable
質問 # 35
What is the route-tag setting in an SD-WAN rule used for?
- A. To indicate the routes that can be used for routing SD-WAN traffic.
- B. To indicate the members that can be used to route SD-WAN traffic.
- C. To indicate the routes for health check probes.
- D. To indicate the destination of a rule based on learned BGP prefixes.
正解:D
質問 # 36
Which two settings can you configure to speed up routing convergence in BGP? (Choose two.)
- A. set-route-tag
- B. holdtime-timer
- C. link-down-failover
- D. update-source
正解:B、C
質問 # 37
Refer to the exhibit.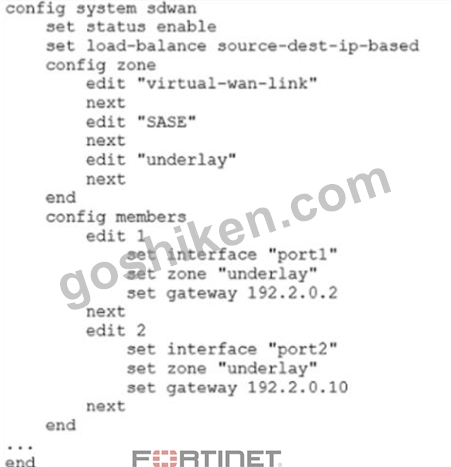
Which algorithm does SD-WAN use to distribute traffic that does not match any of the SD-WAN rules?
- A. All traffic from a source IP is sent to the same interface.
- B. All traffic from a source IP to a destination IP is sent to the same interface.
- C. All traffic from a source IP to a destination IP is sent to the least used interface.
- D. All traffic from a source IP is sent to the most used interface.
正解:B
質問 # 38
Refer to the exhibits.
Exhibit A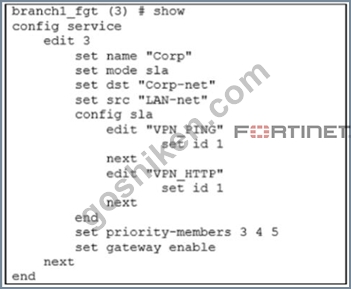
Exhibit B -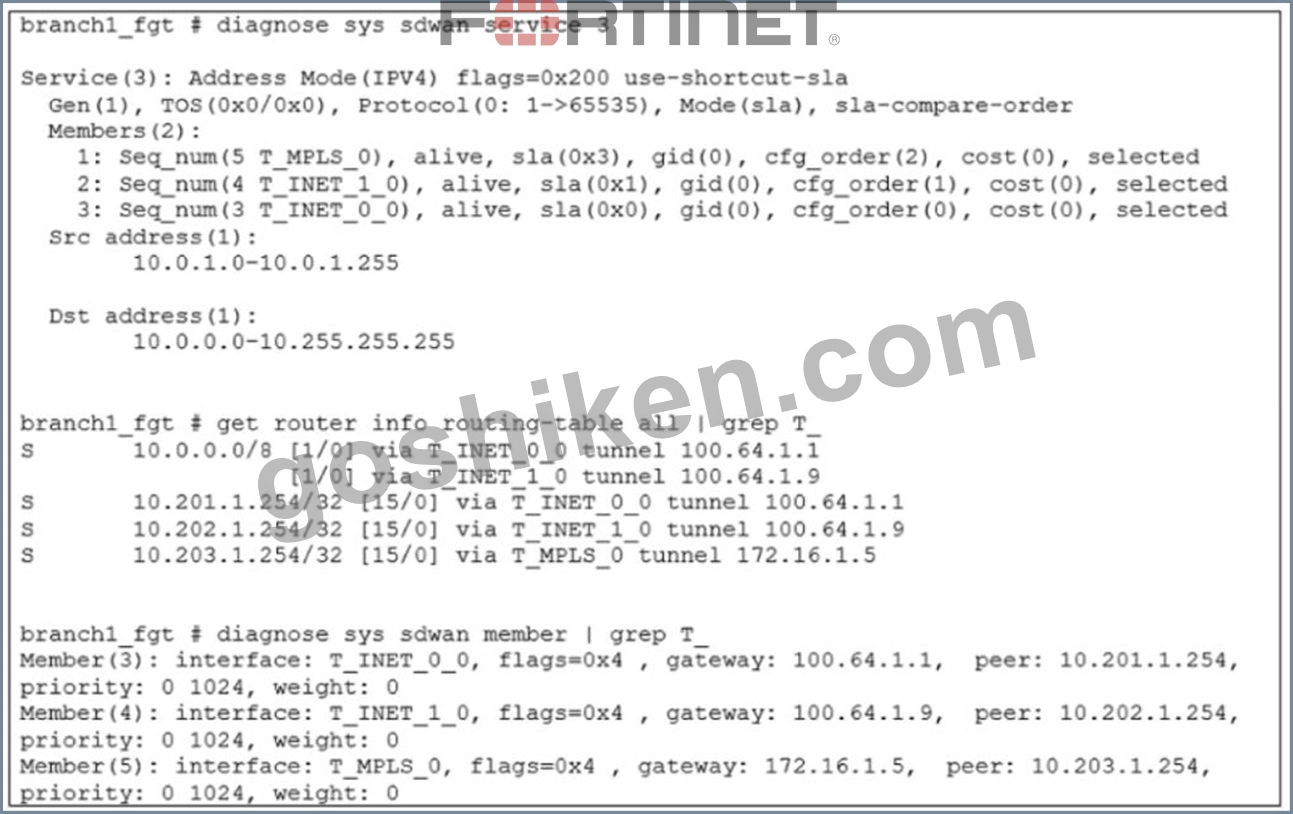
Exhibit A shows the configuration for an SD-WAN rule and exhibit B shows the respective rule status, the routing table, and the member status.
The administrator wants to understand the expected behavior for traffic matching the SD-WAN rule.
Based on the exhibits, what can the administrator expect for traffic matching the SD-WAN rule?
- A. The traffic will be load balanced across all three overlays.
- B. The traffic will be routed over T_INET_0_0.
- C. The traffic will be routed over T_MPLS_0.
- D. The traffic will be routed over T_INET_1_0.
正解:D
質問 # 39
Refer to the exhibits.
Exhibit A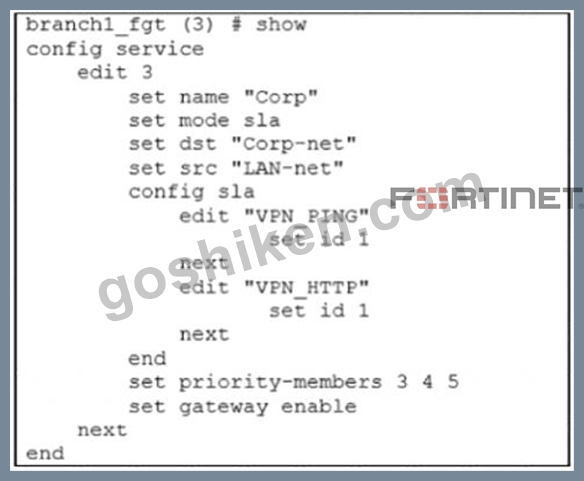
Exhibit B -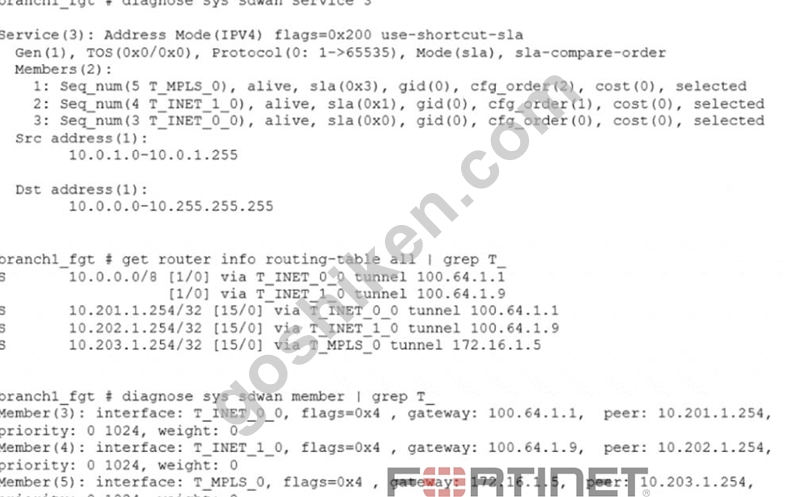
Exhibit A shows the configuration for an SD-WAN rule and exhibit B shows the respective rule status, the routing table, and the member status.
The administrator wants to understand the expected behavior for traffic matching the SD-WAN rule.
Based on the exhibits, what can the administrator expect for traffic matching the SD-WAN rule?
- A. The traffic will be load balanced across all three overlays.
- B. The traffic will be routed over T_MPLS_0.
- C. The traffic will be routed over T_INET_0_0.
- D. The traffic will be routed over T_INET_1_0.
正解:B
質問 # 40
Refer to the exhibit.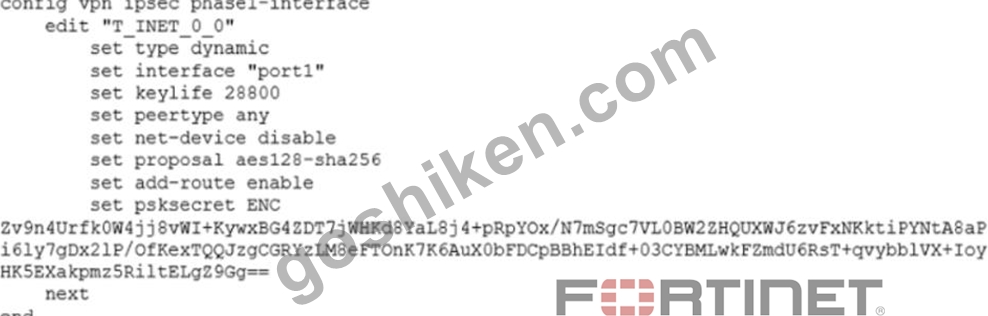
Which configuration change is required if the responder FortiGate uses a dynamic routing protocol to exchange routes over IPsec?
- A. add-route must be disabled.
- B. type must be set to static.
- C. exchange-interface-ip must be enabled.
- D. mode-cfg must be enabled.
正解:A
解説:
for using "non ike" routes (for example BGP/static and so on) you must do disable the add-route that inject automatically kernel route based on p2 selectors from the remote site from the SD-WAN_7.2_Study_Guide page 236
質問 # 41
Refer to the exhibit.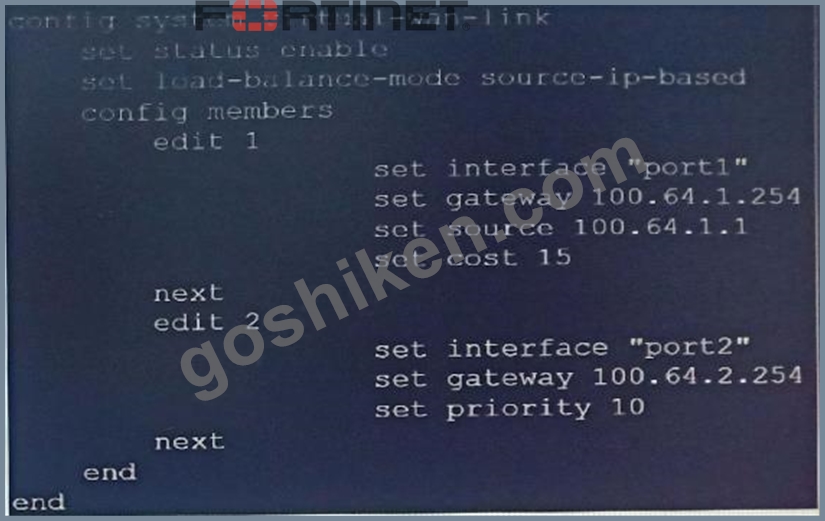
Based on the output shown in the exhibit, which two criteria on the SD-WAN member configuration can be used to select an outgoing interface in an SD-WAN rule? (Choose two.)
- A. Set cost 15.
- B. Set load-balance-mode source-ip-ip-based.
- C. Set source 100.64.1.1.
- D. Set priority 10.
正解:A、D
質問 # 42
Which SD-WAN setting enables FortiGate to delay the recovery of ADVPN shortcuts?
- A. auto-discovery-shortcuts
- B. idle-timeout
- C. hold-down-time
- D. link-down-failover
正解:C
質問 # 43
Which two statements are true about using SD-WAN to steer local-out traffic? (Choose two.)
- A. By default, local-out traffic does not use SD-WAN.
- B. FortiGate does not consider the source address of the packet when matching an SD-WAN rule for local-out traffic.
- C. You must configure each local-out feature individually, to use SD-WAN.
- D. By default, FortiGate does not check if the selected member has a valid route to the destination.
正解:A、C
質問 # 44
Refer to the exhibit.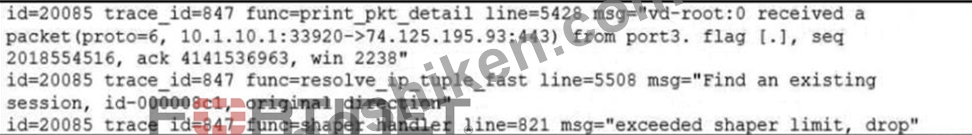
Which conclusion about the packet debug flow output is correct?
- A. The original traffic exceeded the maximum bandwidth of the outgoing interface, and the packet was dropped.
- B. The original traffic exceeded the maximum bandwidth configured in the traffic shaper, and the packet was dropped.
- C. The original traffic exceeded the maximum packets per second of the outgoing interface, and the packet was dropped.
- D. The reply traffic exceeded the maximum bandwidth configured in the traffic shaper, and the packet was dropped.
正解:B
質問 # 45
Which three matching traffic criteria are available in SD-WAN rules? (Choose three.)
- A. URL categories
- B. Source and destination IP address
- C. Internet service database (ISDB) address object
- D. Application signatures
- E. Type of physical link connection
正解:B、C、D
質問 # 46
Refer to the exhibits.
Exhibit A -
Exhibit B -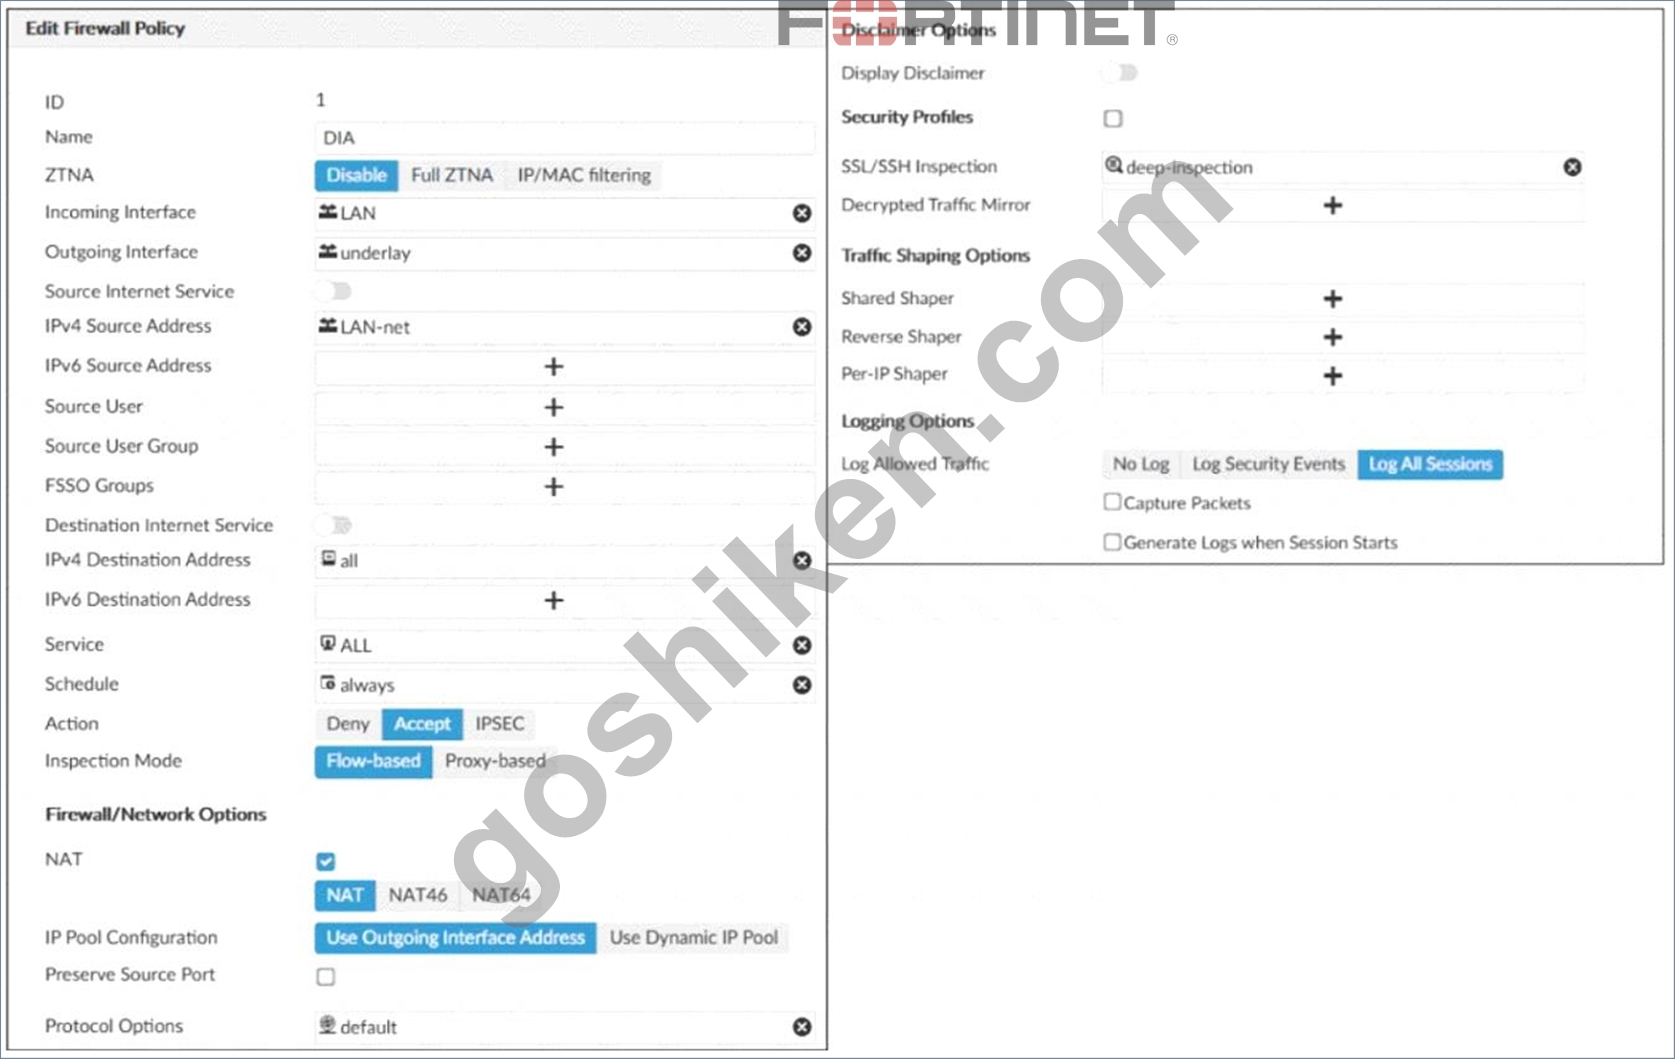
Exhibit A shows the traffic shaping policy and exhibit B shows the firewall policy.
The administrator wants FortiGate to limit the bandwidth used by YouTube. When testing, the administrator determines that FortiGate does not apply traffic shaping on YouTube traffic.
Based on the policies shown in the exhibits, what configuration change must be made so FortiGate performs traffic shaping on YouTube traffic?
- A. Application control must be enabled on the firewall policy.
- B. Destination internet service must be enabled on the traffic shaping policy.
- C. Individual SD-WAN members must be selected as the outgoing interface on the traffic shaping policy.
- D. Web filtering must be enabled on the firewall policy.
正解:A
質問 # 47 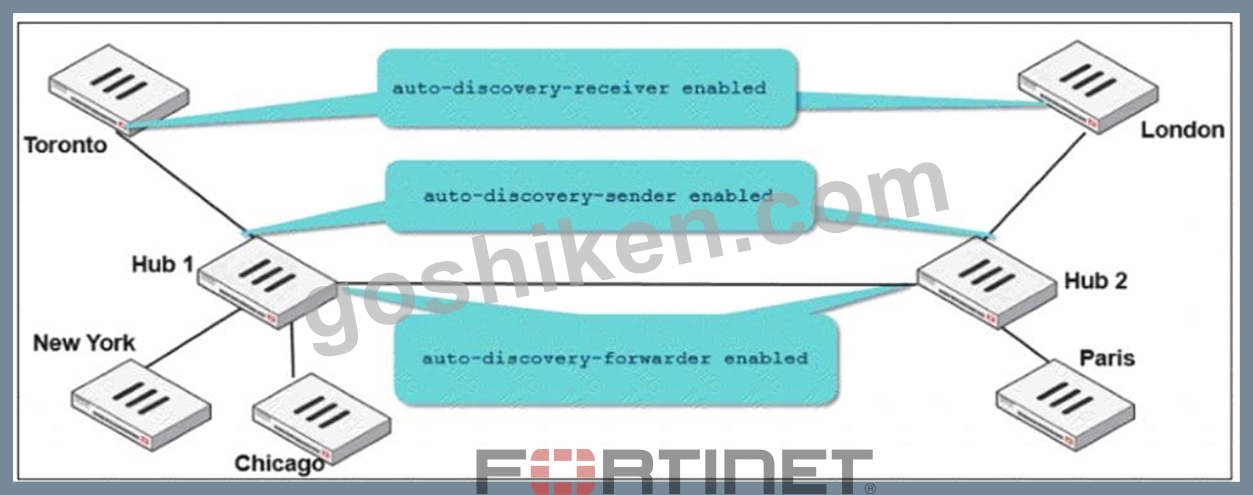
Two hub-and-spoke groups are connected through a site-to-site IPsec VPN between Hub 1 and Hub 2. The administrator configured ADVPN on both hub-and-spoke groups.
Which two outcomes are expected if a user in Toronto sends traffic to London? (Choose two.)
- A. Toronto needs to establish a site-to-site tunnel with Hub 2 to bypass Hub 1.
- B. The first packets from Toronto to London are routed through Hub 1 then to Hub 2.
- C. London generates an IKE information message that contains the Toronto public IP address.
- D. Traffic from Toronto to London triggers the dynamic negotiation of a direct site-to-site VPN.
正解:B、D
質問 # 48
......
Fortinet NSE7_SDW-7.0 試験は、SD-WANに関連する様々なトピックをカバーしており、SD-WANアーキテクチャの設計と実装、SD-WAN展開におけるセキュリティの考慮事項、およびSD-WANネットワークのトラブルシューティングと最適化などが含まれています。この試験に合格した専門家は、安全なSD-WANネットワークを設計、実装、および管理する能力を証明したことになります。
Fortinet NSE7_SDW-7.0問題集PDFのベストを目指すなら問題集を使おう 目指そう高得点:https://www.goshiken.com/Fortinet/NSE7_SDW-7.0-mondaishu.html
NSE 7 Network Security Architect NSE7_SDW-7.0試験と認定テストエンジン:https://drive.google.com/open?id=17R6fQf9P1cI8XtYzJtihin_Hin3tILMf