
2024年最新の有効なAZ-500リアル試験問題(更新された)100%問題集と練習試験合格させます
[更新されたのは2024年]Microsoft AZ-500問題準備には無料サンプルのPDF
質問 # 224
You have an Azure subscription that contains an Azure SQL database named SQLDB1. SQLDB1 contains the columns shown in the following table.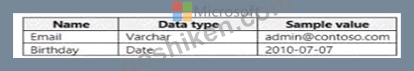
For the Email and Birthday columns, you implement dynamic data masking by using the default masking function.
Which value will the users see in each column? To answer, drag the appropriate values to the correct columns.
Each value may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.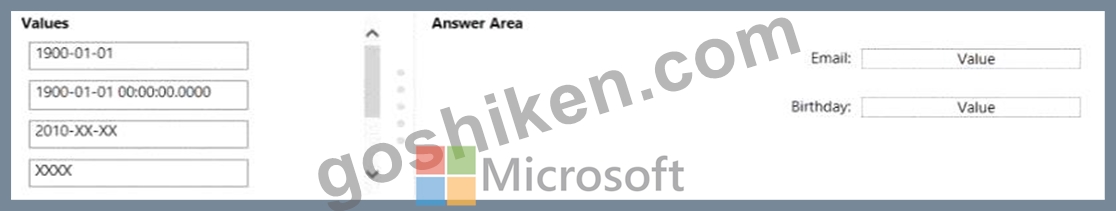
正解:
解説: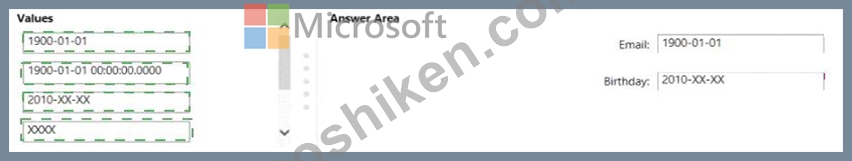
Explanation: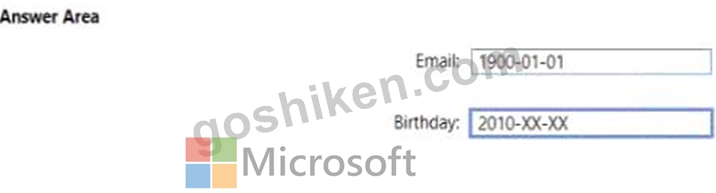
質問 # 225
You create resources in an Azure subscription as shown in the following table.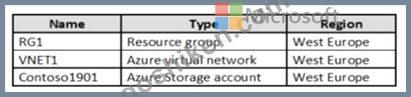
VNET1 contains two subnets named Subnet1 and Subnet2. Subnet1 has a network ID of 10.0.0.0/24. Subnet2 has a network ID of 10.1.1.0/24.
Contoso1901 is configured as shown in the exhibit. (Click the Exhibit tab.)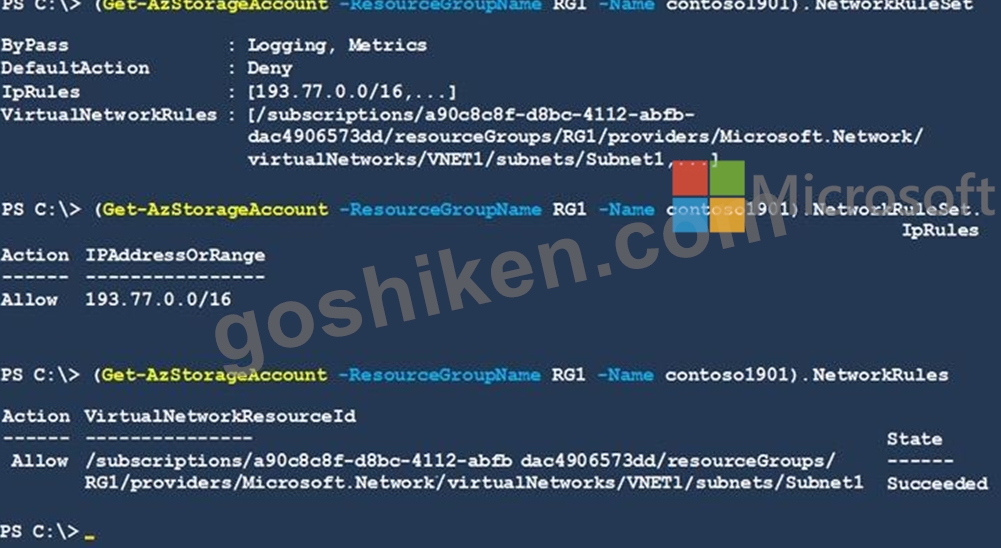
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.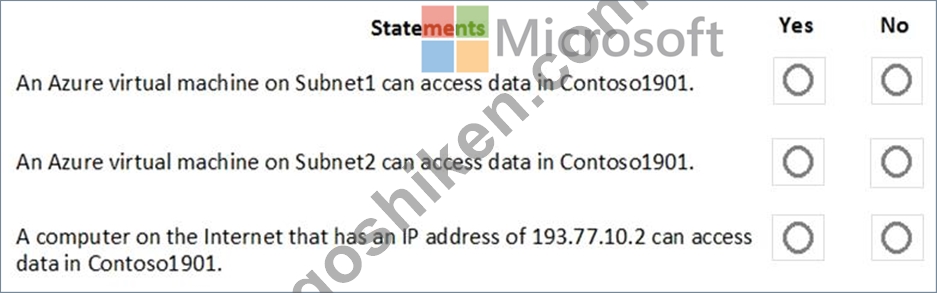
正解:
解説: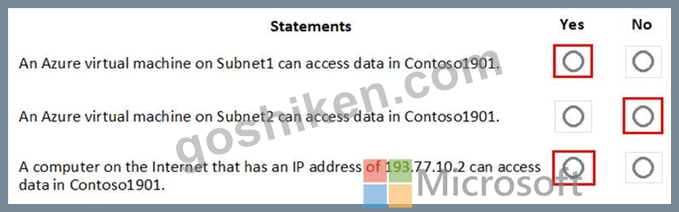
Explanation:
Box 1: Yes
Access from Subnet1 is allowed.
Box 2: No
No access from Subnet2 is allowed.
Box 3: Yes
Access from IP address 193.77.10.2 is allowed.
質問 # 226
You create an Azure subscription.
You need to ensure that you can use Azure Active Directory (Azure AD) Privileged Identity Management (PIM) to secure Azure AD roles.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.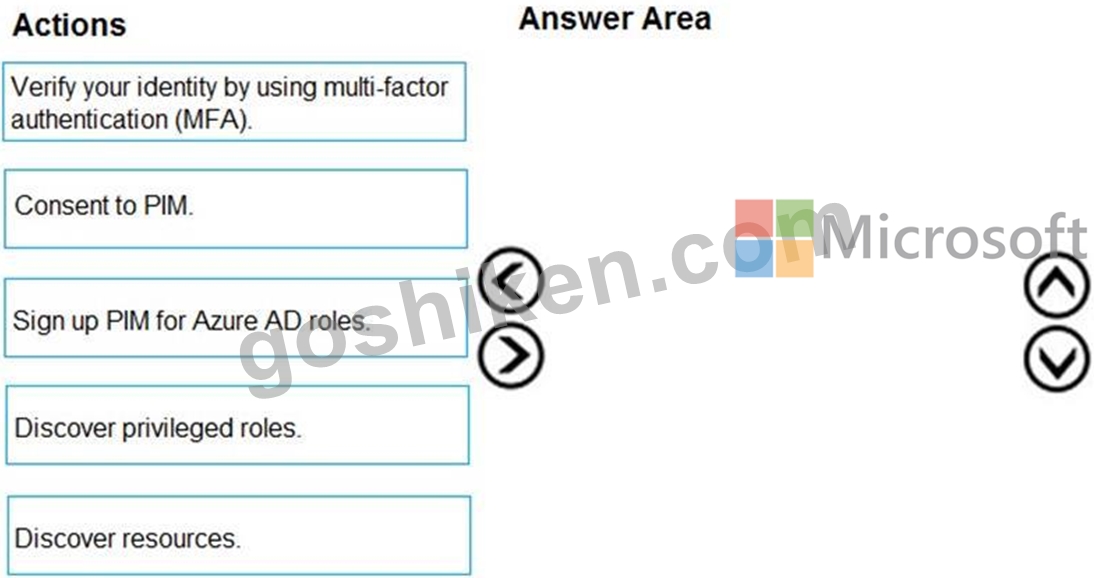
正解:
解説: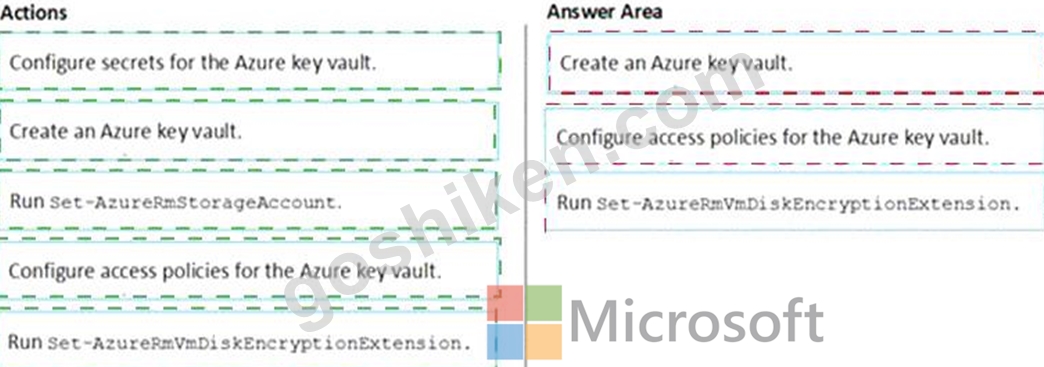
Explanation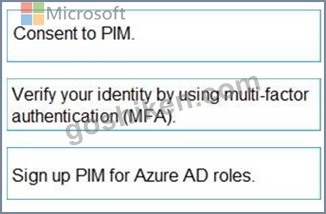
Step 1: Consent to PIM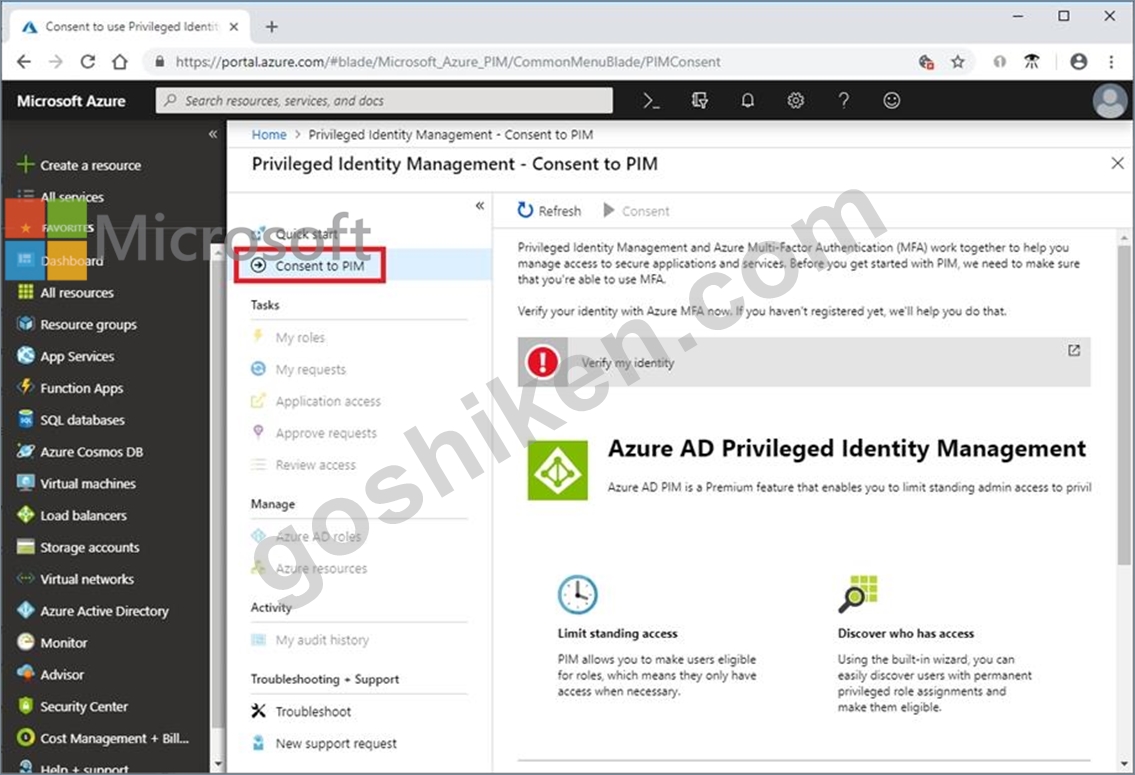
Step: 2 Verify your identity by using multi-factor authentication (MFA) Click Verify my identity to verify your identity with Azure MFA. You'll be asked to pick an account.
Step 3: Sign up PIM for Azure AD roles
Once you have enabled PIM for your directory, you'll need to sign up PIM to manage Azure AD roles.
References:
https://docs.microsoft.com/en-us/azure/active-directory/privileged-identity-management/pim-getting-started
質問 # 227
You suspect that users are attempting to sign in to resources to which they have no access.
You need to create an Azure Log Analytics query to identify failed user sign-in attempts from the last three days. The results must only show users who had more than five failed sign-in attempts.
How should you configure the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.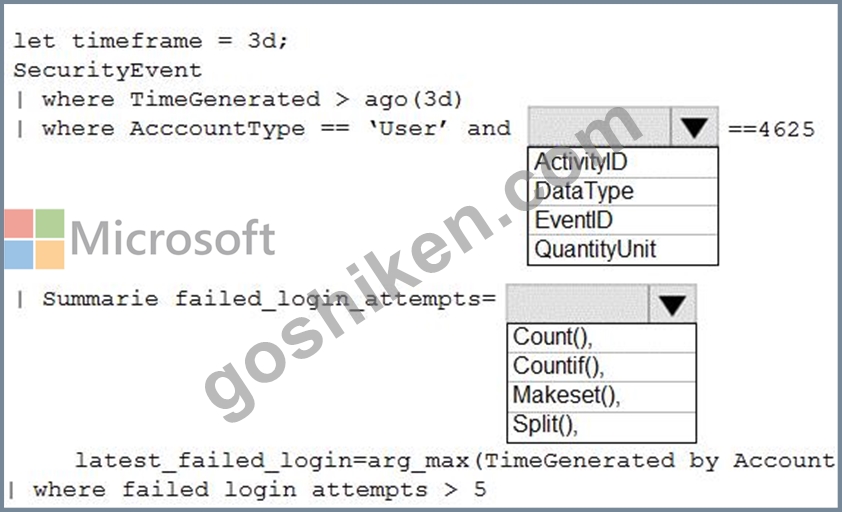
正解:
解説: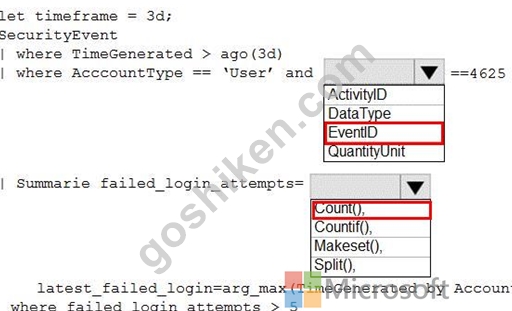
Reference:
https://docs.microsoft.com/en-us/azure/azure-monitor/log-query/examples
質問 # 228
You have an Azure Container Registry named Registry1.
You add role assignment for Registry1 as shown in the following table.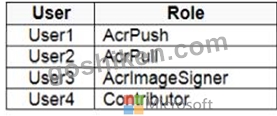
Which users can upload images to Registry1 and download images from Registry1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.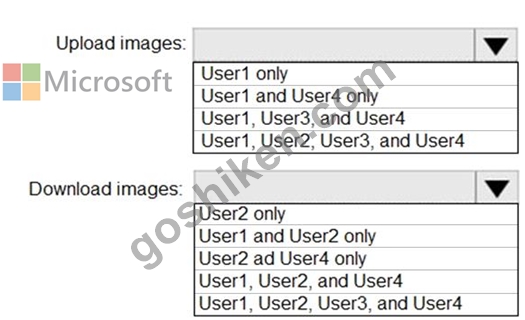
正解:
解説: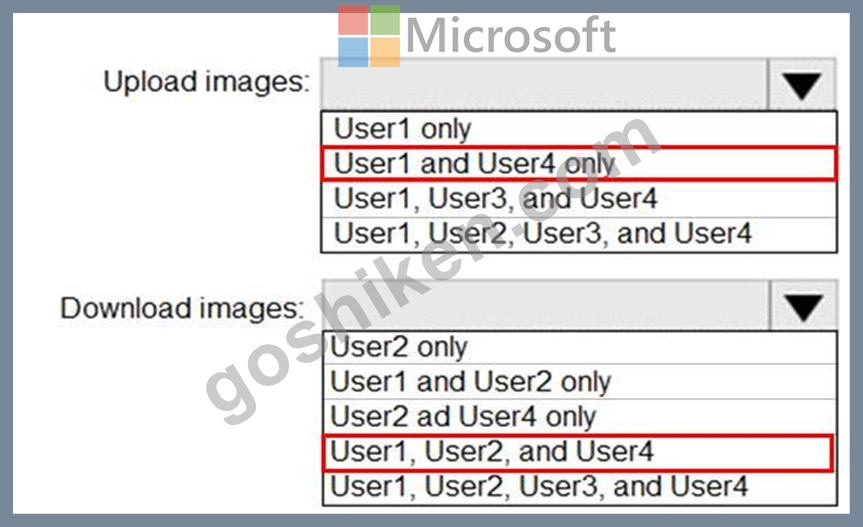
References:
https://docs.microsoft.com/bs-latn-ba/azure/container-registry/container-registry-roles
質問 # 229
You have an Azure subscription named Sub1 that contains an Azure Log Analytics workspace named LAW1.
You have 500 Azure virtual machines that run Windows Server 2016 and are enrolled in LAW1.
You plan to add the System Update Assessment solution to LAW1.
You need to ensure that System Update Assessment-related logs are uploaded to LAW1 from 100 of the virtual machines only.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.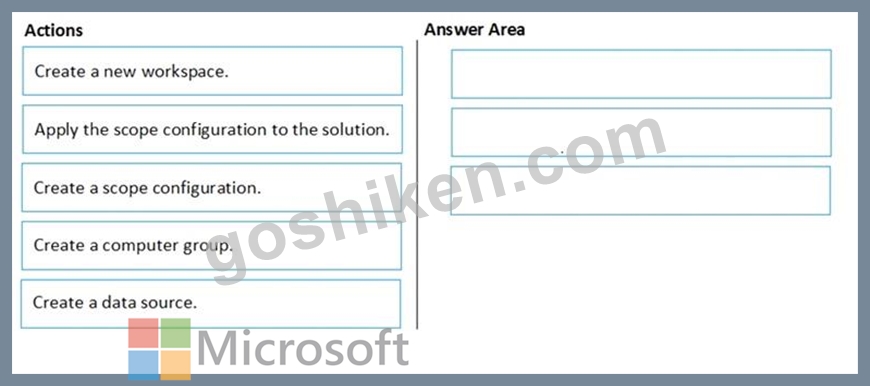
正解:
解説: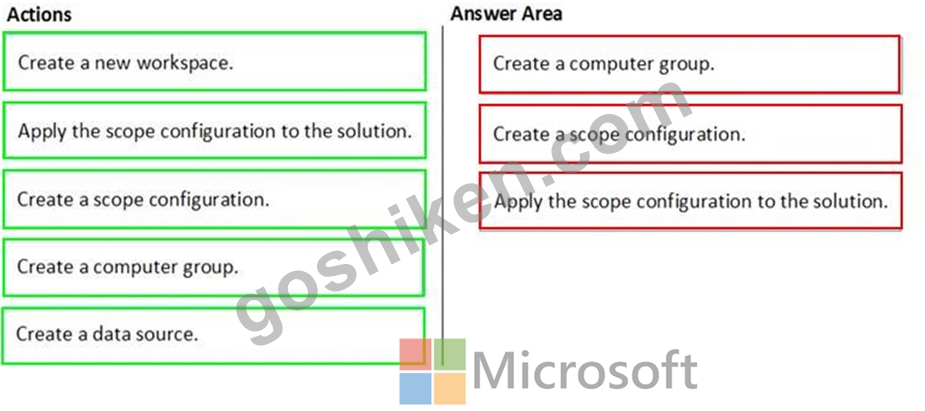
Explanation:
References:
https://docs.microsoft.com/en-us/azure/azure-monitor/insights/solution-targeting
質問 # 230
You are evaluating the security of VM1, VM2, and VM3 in Sub2.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
正解:
解説: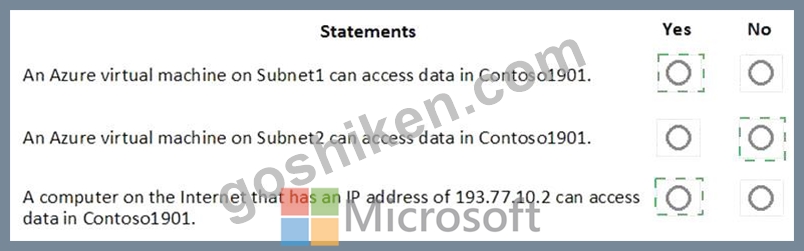
Explanation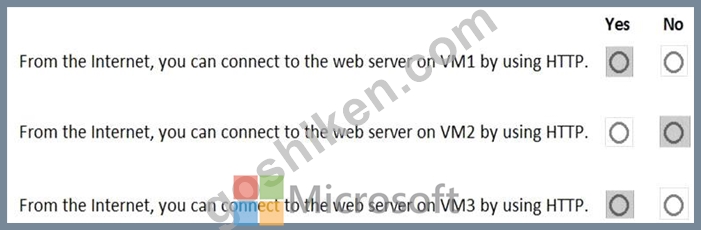
質問 # 231
You are evaluating the security of VM1, VM2, and VM3 in Sub2.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
正解:
解説: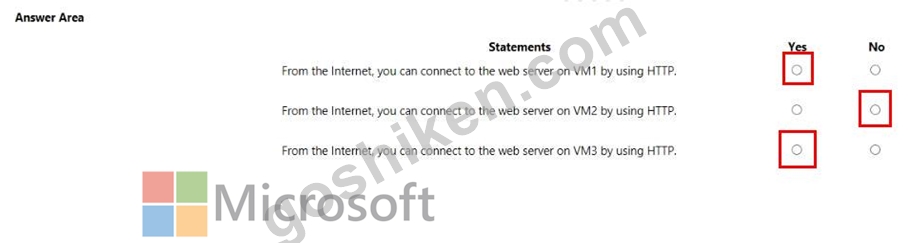
質問 # 232
You have an Azure subscription that contains the resources shown in the following table.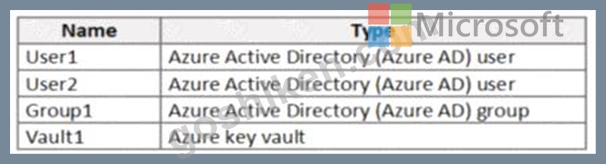
User1 is a member of Group1. Group1 and User2 are assigned the Key Vault Contributor role for Vault1.
On January 1, 2019, you create a secret in Vault1. The secret is configured as shown in the exhibit. (Click the Exhibit tab.)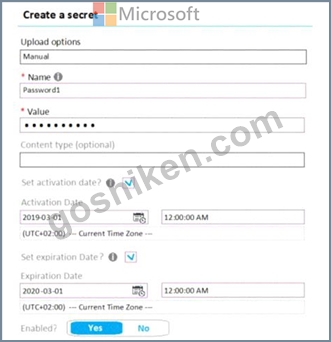
User2 is assigned an access policy to Vault1. The policy has the following configurations:
Key Management Operations: Get, List, and Restore
Cryptographic Operations: Decrypt and Unwrap Key
Secret Management Operations: Get, List, and Restore
Group1 is assigned an access to Vault1. The policy has the following configurations:
Key Management Operations: Get and Recover
Secret Management Operations: List, Backup, and Recover
For each of the following statements, select Yes if the statement is true. Otherwise, select No.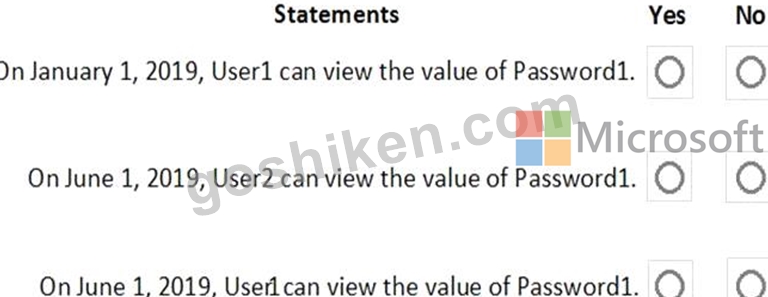
正解:
解説: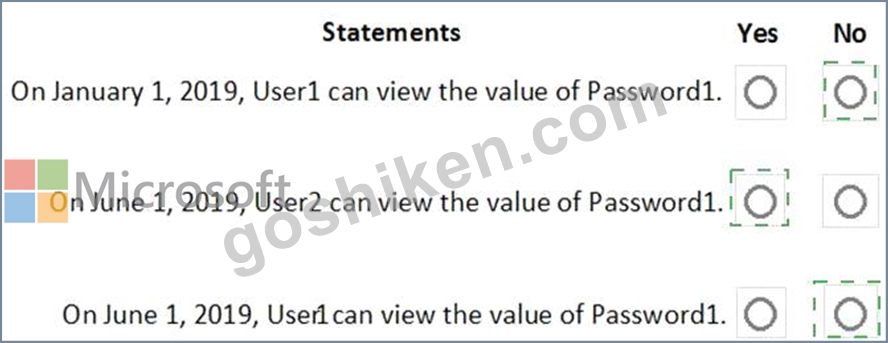
Explanation: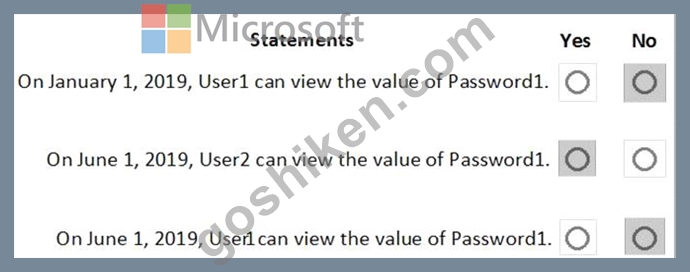
質問 # 233
You have an Azure subscription named Sub1 that contains an Azure Log Analytics workspace named LAW1.
You have 500 Azure virtual machines that run Windows Server 2016 and are enrolled in LAW1.
You plan to add the System Update Assessment solution to LAW1.
You need to ensure that System Update Assessment-related logs are uploaded to LAW1 from 100 of the virtual machines only.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.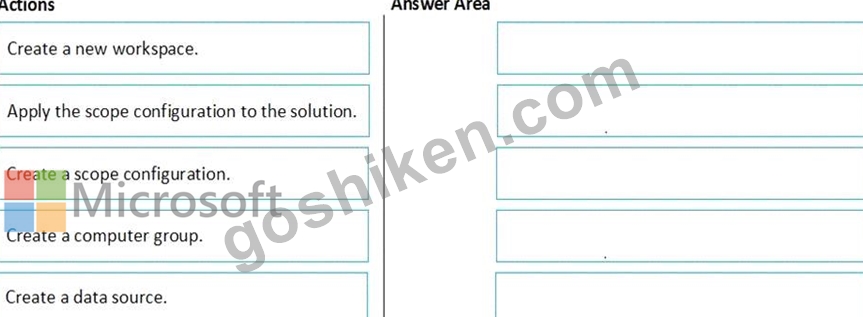
正解:
解説: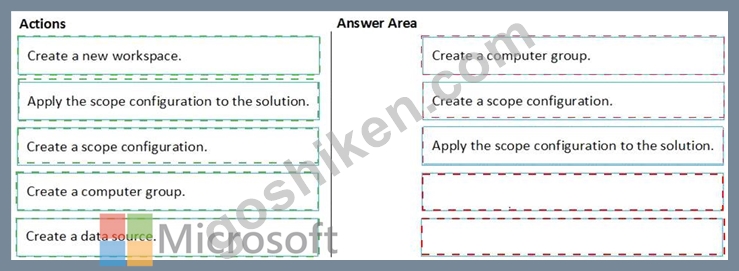
Explanation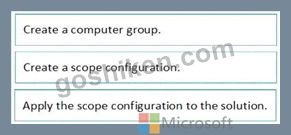
References:
https://docs.microsoft.com/en-us/azure/azure-monitor/insights/solution-targeting
質問 # 234
You have an Azure subscription named Sub1 that contains the virtual machines shown in the following table.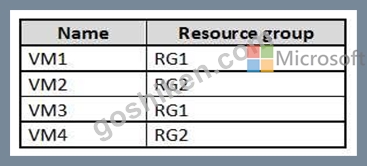
You need to ensure that the virtual machines in RG1 have the Remote Desktop port closed until an authorized user requests access.
What should you configure?
- A. Azure Active Directory (Azure AD) Privileged Identity Management (PIM)
- B. an application security group
- C. Azure Active Directory (Azure AD) conditional access
https://www.fast2test.com/AZ-500-practice-test.html 75
Valid Fast2test AZ-500 Exam PDF Dumps - New AZ-500 Real Exam Questions - D. just in time (JIT) VM access
正解:D
解説:
Just-in-time (JIT) virtual machine (VM) access can be used to lock down inbound traffic to your Azure VMs, reducing exposure to attacks while providing easy access to connect to VMs when needed.
Note: When just-in-time is enabled, Security Center locks down inbound traffic to your Azure VMs by creating an NSG rule. You select the ports on the VM to which inbound traffic will be locked down. These ports are controlled by the just-in-time solution.
When a user requests access to a VM, Security Center checks that the user has Role-Based Access Control (RBAC) permissions that permit them to successfully request access to a VM. If the request is approved, Security Center automatically configures the Network Security Groups (NSGs) and Azure Firewall to allow inbound traffic to the selected ports and requested source IP addresses or ranges, for the amount of time that was specified. After the time has expired, Security Center restores the NSGs to their previous states. Those connections that are already established are not being interrupted, however.
Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-just-in-time
質問 # 235
You create an Azure subscription with Azure AD Premium P2.
You need to ensure that you can use Azure Active Directory (Azure AD) Privileged Identity Management (PIM) to secure Azure roles.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.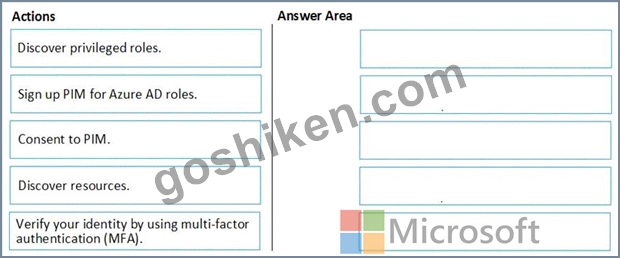
正解:
解説: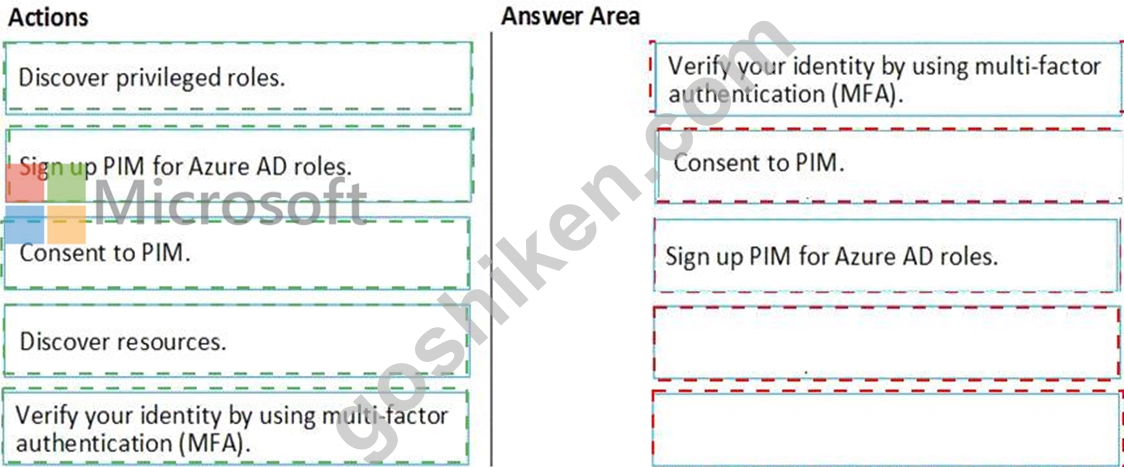
Explanation
1. Verify your identity with MFA
2. Consent to PIM
3. Sign up PIM for AAD Roles
質問 # 236
You are configuring network connectivity for two Azure virtual networks named VNET1 and VNET2.
You need to implement VPN gateways for the virtual networks to meet the following requirements:
* VNET1 must have six site-to-site connections that use BGP.
* VNET2 must have 12 site-to-site connections that use BGP.
* Costs must be minimized.
Which VPN gateway SKI) should you use for each virtual network? To answer, drag the appropriate SKUs to the correct networks. Each SKU may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point
正解:
解説: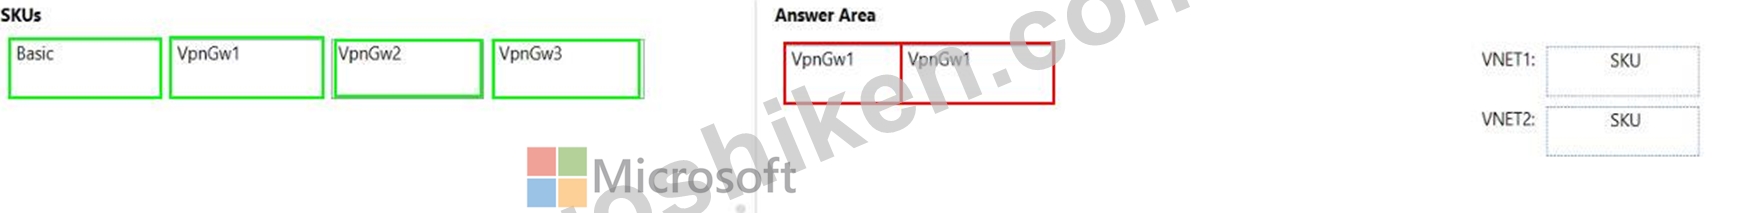
Reference:
https://docs.microsoft.com/en-us/azure/vpn-gateway/vpn-gateway-about-vpngateways#gwsku
質問 # 237
You have the hierarchy of Azure resources shown in the following exhibit.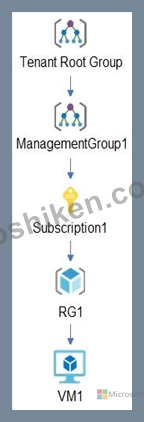
You create the Azure Blueprints definitions shown in the following table.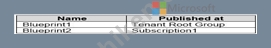
To which objects can you assign Blueprint1 and Blueprint2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.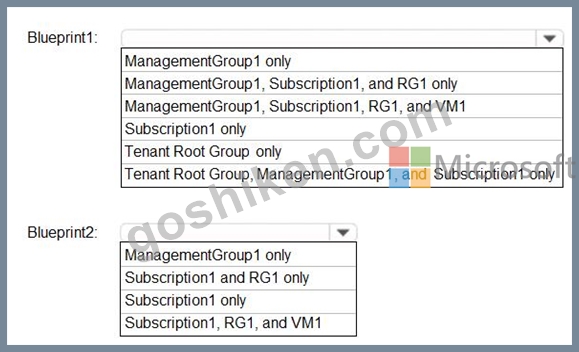
正解:
解説: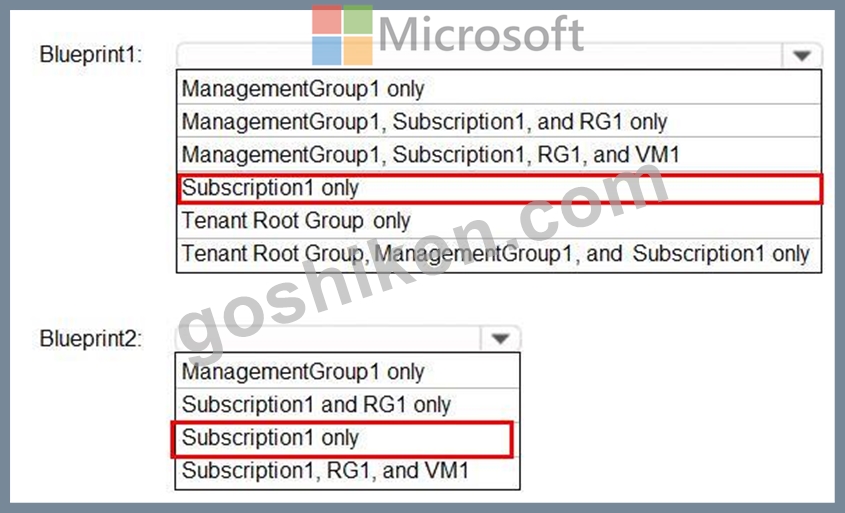
Explanation:
Blueprints can only be assigned to subscriptions.
質問 # 238
You have an Azure Active Din-dory (Azure AD) tenant named contoso.com that contains a user named User1.
You plan to publish several apps in the tenant.
You need to ensure that User1 can grant admin consent for the published apps.
Which two possible user roles can you assign to User! to achieve this goal? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. Cloud application administrator
- B. Application administrator
- C. User administrator
- D. Security administrator
- E. Application developer
正解:C、E
質問 # 239
You have a management group named MG1 that contains an Azure subscription and a resource group named RG1. RG1 contains a virtual machine named VM1. You have the custom Azure roles shown in the following table.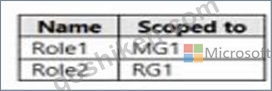
The permissions for Role1 are shown in the following role definition file.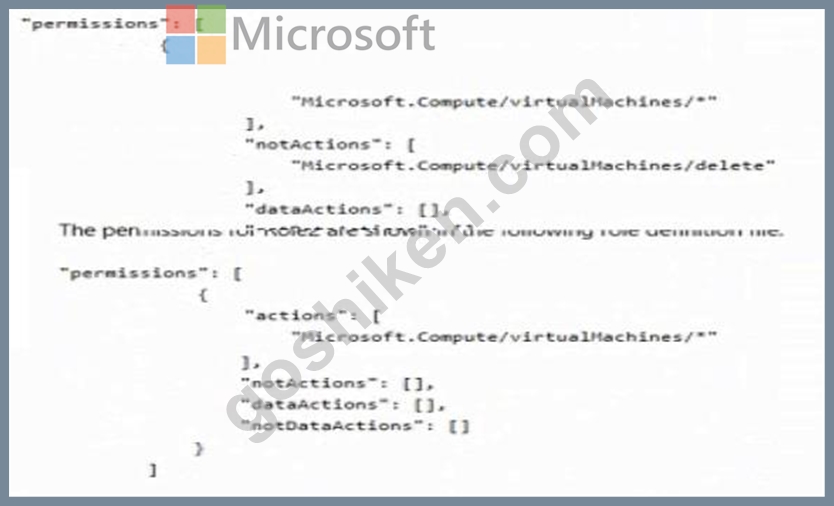
You assign the roles to the users shown in the following table.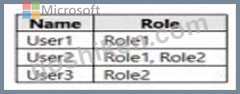
For each of the following statements, select Yes if the statement is true. Otherwise, select No NOTE: Each correct selection is worth one point.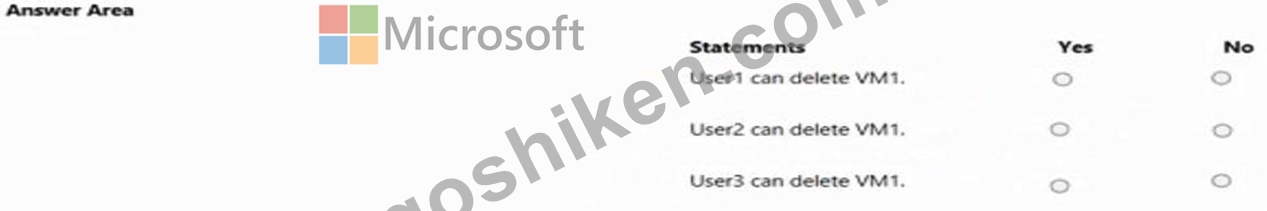
正解:
解説: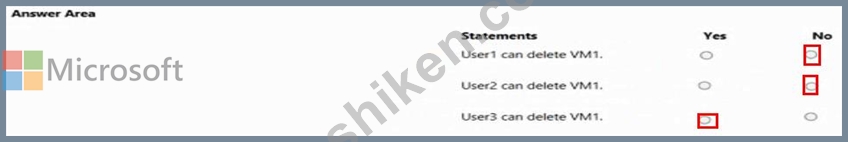
質問 # 240
Your company has an Azure subscription named Sub1 that is associated to an Azure Active Directory Azure
(Azure AD) tenant named contoso.com.
The company develops a mobile application named App1. App1 uses the OAuth 2 implicit grant type to acquire
Azure AD access tokens.
You need to register App1 in Azure AD.
What information should you obtain from the developer to register the application?
- A. an application ID
- B. a key
- C. a reply URL
- D. a redirect URI
正解:D
解説:
For Native Applications you need to provide a Redirect URI, which Azure AD will use to return token
responses.
References:
https://docs.microsoft.com/en-us/azure/active-directory/develop/v1-protocols-oauth-code
質問 # 241
You have an Azure subscription that contains an Azure Sentinel workspace.
Azure Sentinel is configured to ingest logs from several Azure workloads. A third-party service management platform is used to manage incidents.
You need to identify which Azure Sentinel components to configure to meet the following requirements:
When Azure Sentinel identifies a threat, an incident must be created.
A ticket must be logged in the service management platform when an incident is created in Azure Sentinel.
Which component should you identify for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.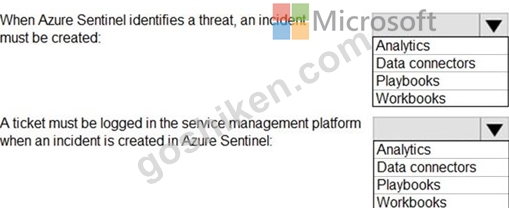
正解:
解説: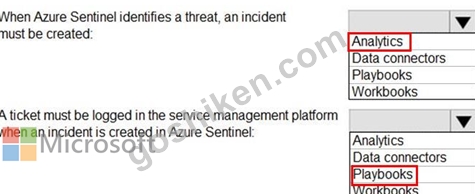
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/create-incidents-from-alerts
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-respond-threats-playbook
質問 # 242
You have Azure virtual machines that have Update Management enabled. The virtual machines are configured as shown in the following table.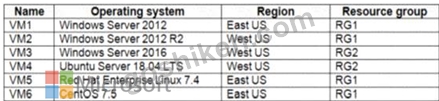
You schedule two update deployments named Update1 and Update2. Update1 updates VM3. Update2 updates VM6.
Which additional virtual machines can be updated by using Update1 and Update2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.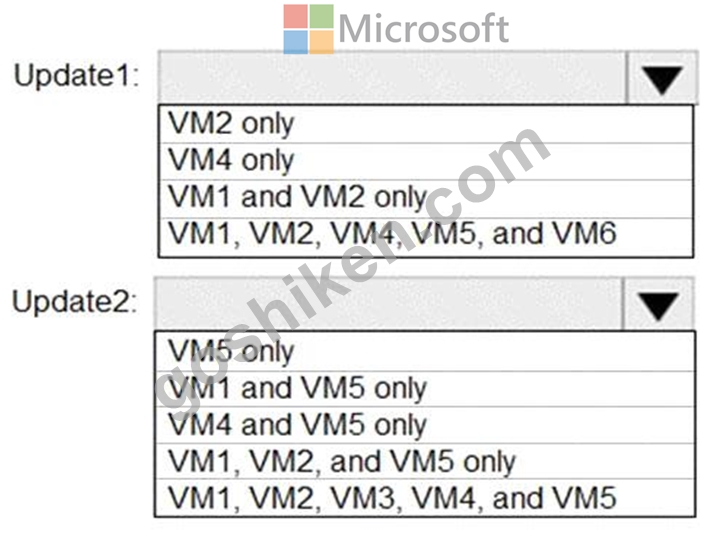
正解:
解説: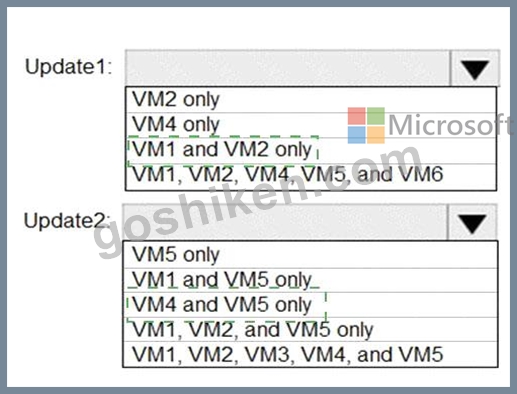
Explanation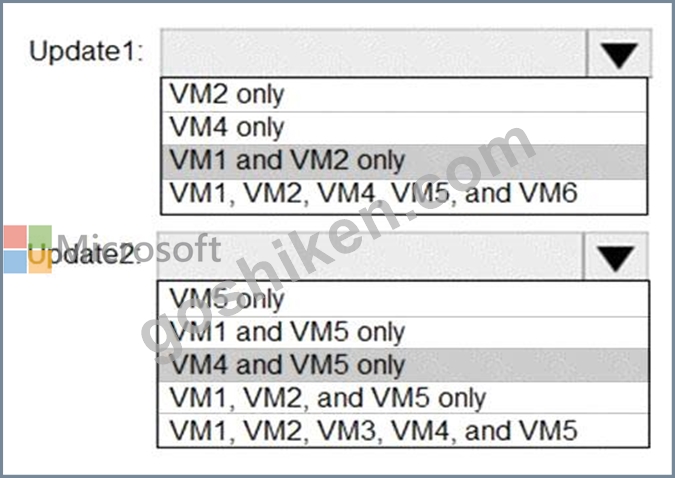
Update1: VM1 and VM2 only
VM3: Windows Server 2016 West US RG2
Update2: VM4 and VM5 only
VM6: CentOS 7.5 East US RG1
For Linux, the machine must have access to an update repository. The update repository can be private or public.
References:
https://docs.microsoft.com/en-us/azure/automation/automation-update-management
質問 # 243
You have an Azure subscription that contains the resources shown in the following table.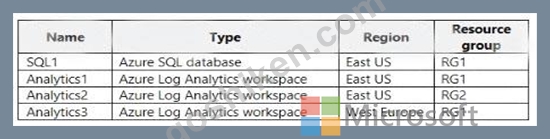
You create the Azure Storage accounts shown in the following table.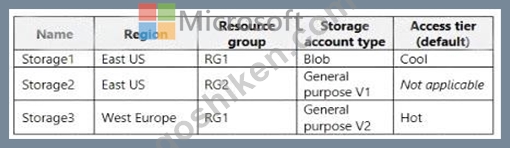
You need to configure auditing for SQL1.
Which storage accounts and Log Analytics workspaces can you use as the audit log destination? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.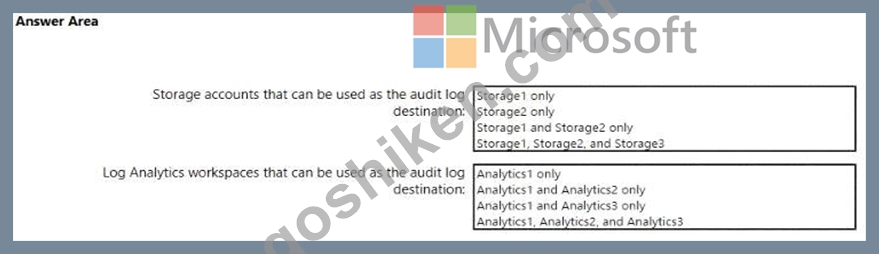
正解:
解説: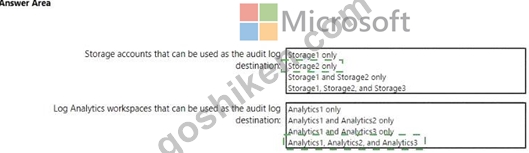
Explanation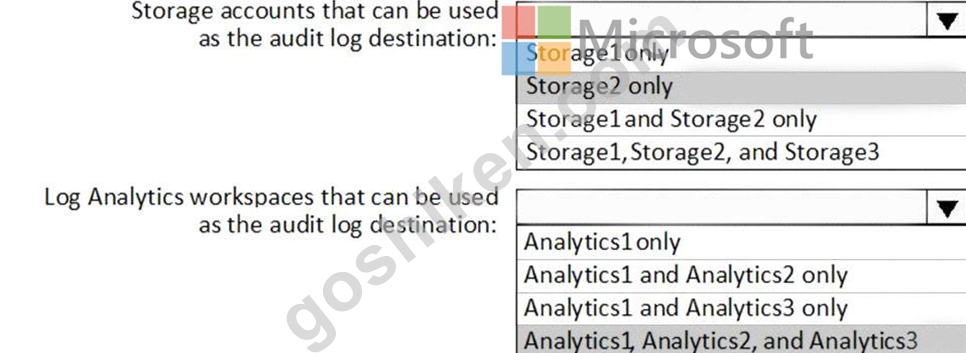
質問 # 244
You have a Microsoft Entra tenant that contains a user named User1.
You plan to enable passwordless authentication for the tenant.
You need to ensure that User1 can enable the combined registration experience. The solution must use the principle of least privilege.
Which role should you assign to User1?
- A. Authentication Administrator
- B. Privileged Role Administrator
- C. Security Administrator
- D. Global Administrator
正解:A
質問 # 245
You need to ensure that the rg1lod10598168n1 Azure Storage account is encrypted by using a key stored in the KeyVault10598168 Azure key vault.
To complete this task, sign in to the Azure portal.
正解:
解説:
See the explanation below.
Explanation
Step 1: To enable customer-managed keys in the Azure portal, follow these steps:
1. Navigate to your storage account rg1lod10598168n1
2. On the Settings blade for the storage account, click Encryption. Select the Use your own key option, as shown in the following figure.
Graphical user interface, text, application, email Description automatically generated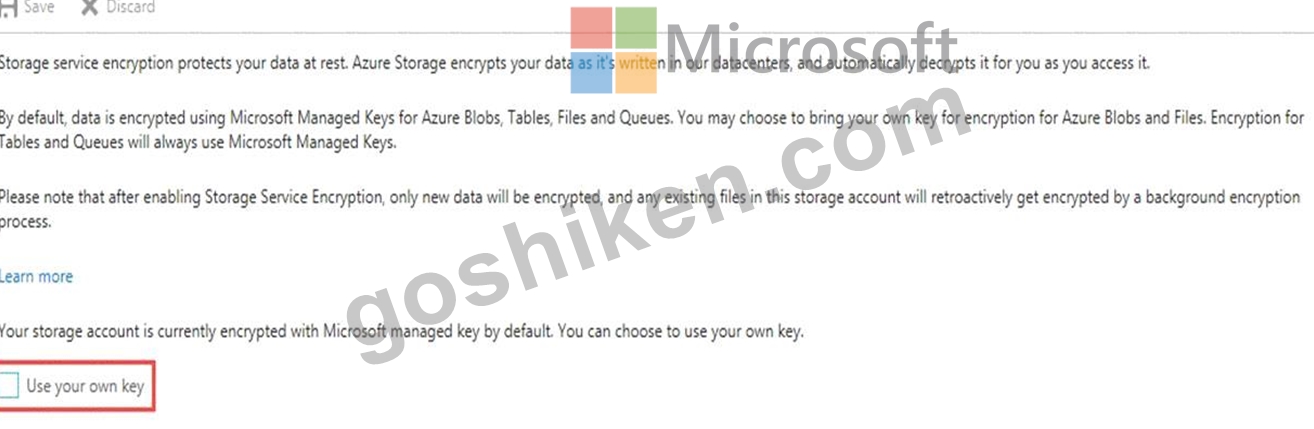
Step 2: Specify a key from a key vault
To specify a key from a key vault, first make sure that you have a key vault that contains a key. To specify a key from a key vault, follow these steps:
4. Choose the Select from Key Vault option.
5. Choose the key vault KeyVault10598168 containing the key you want to use.
6. Choose the key from the key vault.
Graphical user interface, text, application, email Description automatically generated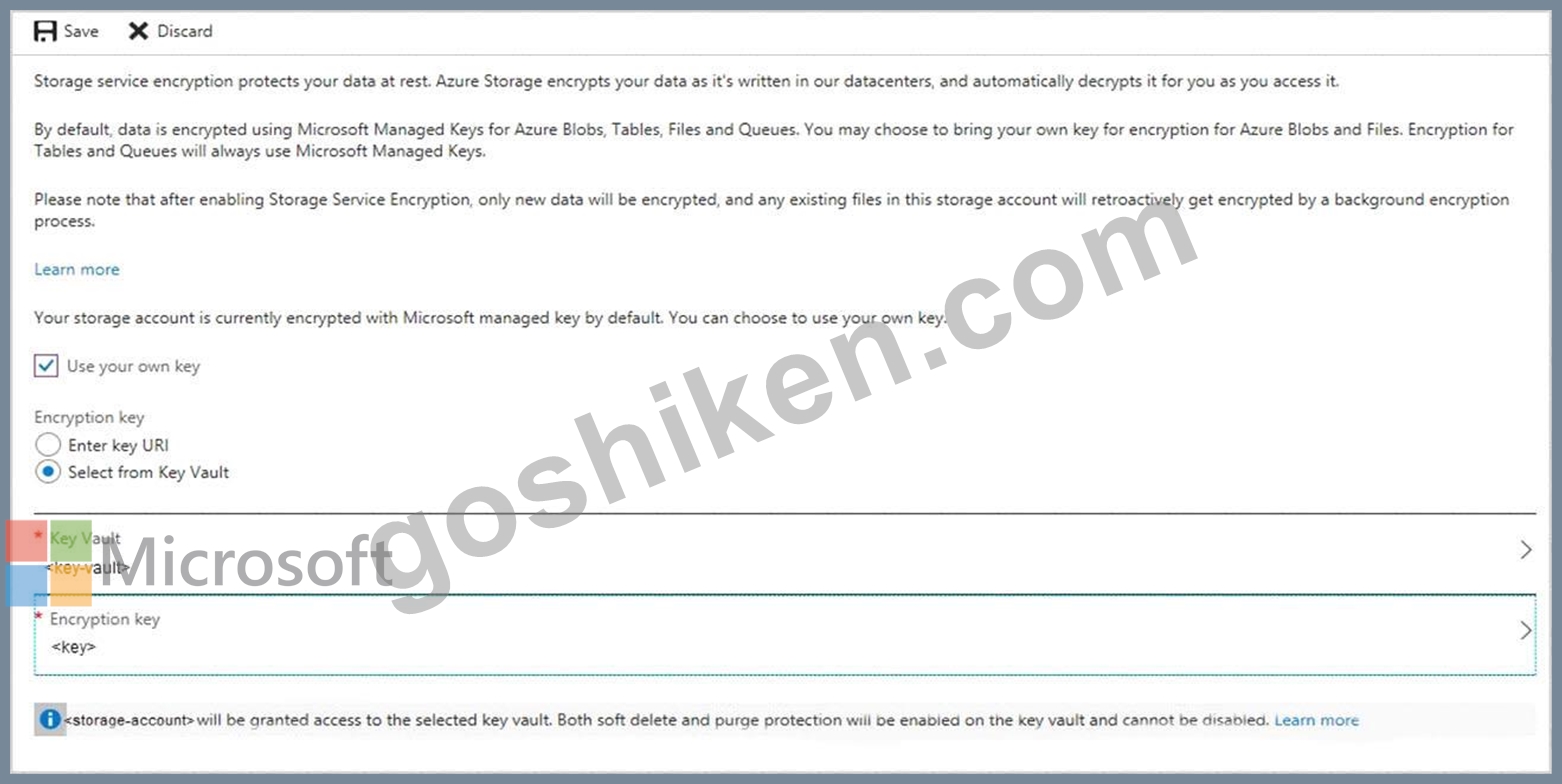
Reference:
https://docs.microsoft.com/en-us/azure/storage/common/storage-encryption-keys-portal
質問 # 246
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure Subscription named Sub1. Sub1 contains an Azure virtual machine named VM1 that runs Windows Server 2016.
You need to encrypt VM1 disks by using Azure Disk Encryption.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.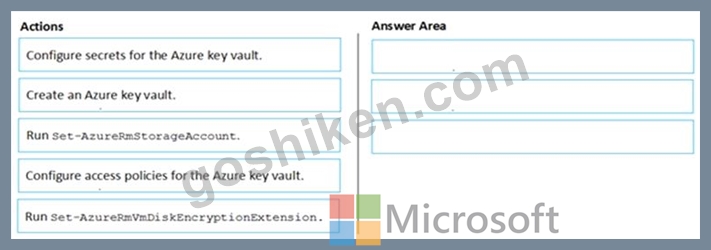
正解:
解説: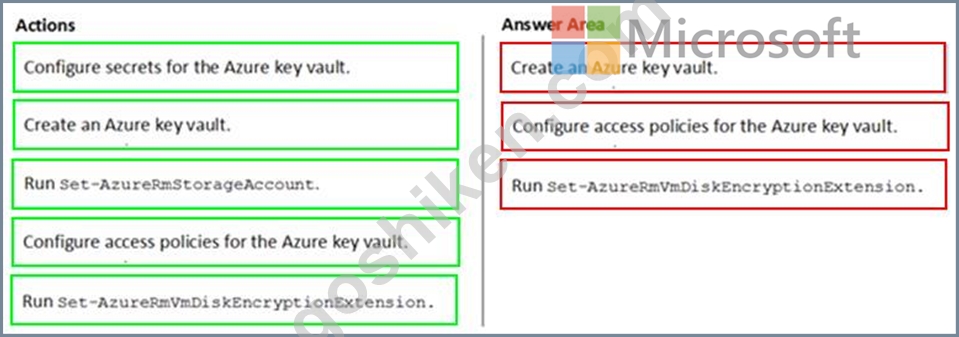
Explanation:
References:
https://docs.microsoft.com/en-us/azure/virtual-machines/windows/encrypt-disks
質問 # 247
You have an Azure subscription named Sub1. Sub1 contains a virtual network named VNet1 that contains one subnet named Subnet1.
You create a service endpoint for Subnet1.
Subnet1 contains an Azure virtual machine named VM1 that runs Ubuntu Server 18.04.
You need to deploy Docker containers to VM1. The containers must be able to access Azure Storage resources and Azure SQL databases by using the service endpoint.
- A. Install the container network interface (CNI) plug-in.
- B. Create an application security group and a network security group (NSG).
- C. Edit the docker-compose.yml file.
正解:A
解説:
The Azure Virtual Network container network interface (CNI) plug-in installs in an Azure Virtual Machine.
The plug-in supports both Linux and Windows platform.
The plug-in assigns IP addresses from a virtual network to containers brought up in the virtual machine, attaching them to the virtual network, and connecting them directly to other containers and virtual network resources. The plug-in doesn't rely on overlay networks, or routes, for connectivity, and provides the same performance as virtual machines.
The following picture shows how the plug-in provides Azure Virtual Network capabilities to Pods: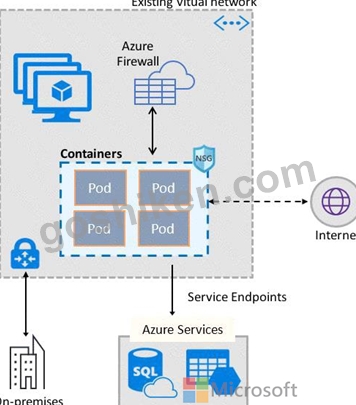
References:
https://docs.microsoft.com/en-us/azure/virtual-network/container-networking-overview
質問 # 248
You have an Azure subscription named Subscription1 that contains the resources shown in the following table.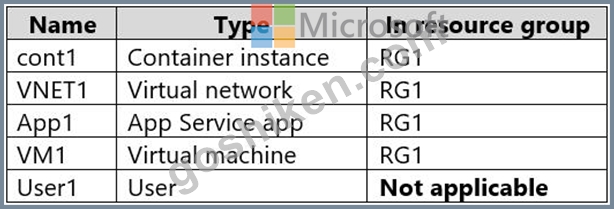
You create a custom RBAC role in Subscription1 by using the following JSON file.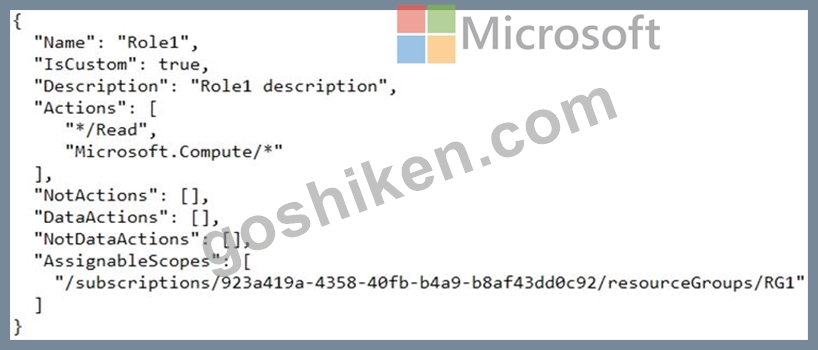
You assign Role1 to User1 on RG1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.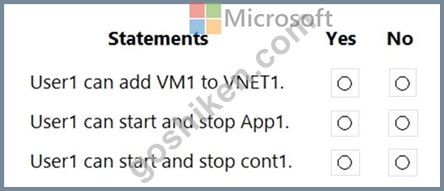
正解:
解説: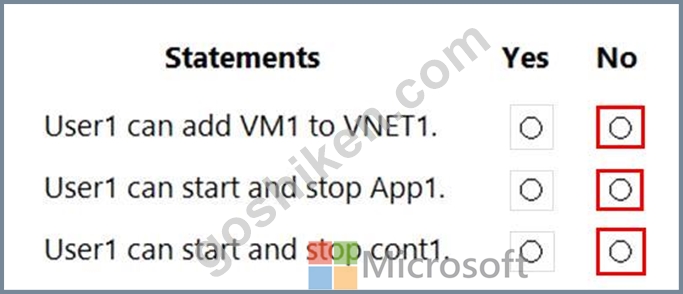
Reference:
https://docs.microsoft.com/en-us/azure/role-based-access-control/resource-provider-operations#microsoftcompute
質問 # 249
......
AZ-500豪華セット学習ガイドにはオンライン試験エンジン:https://www.goshiken.com/Microsoft/AZ-500-mondaishu.html
2024年最新の認定サンプル問題AZ-500問題集と練習試験:https://drive.google.com/open?id=1mjd2YldiodlwbjqIKOhdLYbo_K69zzfd