

最新2024年12月23日リアルなNSE6_WCS-7.0試験問題集解答で有効なNSE6_WCS-7.0問題集PDF
Fortinet NSE6_WCS-7.0試験問題集でPDF問題とテストエンジン
Fortinet NSE6_WCS-7.0試験は、AWS上のクラウドセキュリティに関連するさまざまなトピックをカバーしており、AWSインフラストラクチャ、セキュリティグループ、ネットワークACL、VPN接続などが含まれます。候補者は、セキュリティリスクと脆弱性を特定する能力、およびこれらのリスクを緩和するセキュリティソリューションを実装する能力を示さなければなりません。さらに、この試験では、Fortinetのクラウドセキュリティソリューション、FortiGate、FortiAnalyzer、FortiManagerに関する候補者の知識もテストされます。
Fortinet NSE6_WCS-7.0認定試験は、Amazon Web Services(AWS)プラットフォームでクラウド環境を確保することに関心のある個人の知識とスキルを検証するように設計されています。この認定は、クラウド環境でセキュリティソリューションの実装と管理に習熟したいと考えているセキュリティの専門家に最適です。
Fortinet NSE6_WCS-7.0認定は、AWSプラットフォーム上のクラウドベースのアプリケーションとサービスのセキュリティを担当するセキュリティプロフェッショナル、ネットワーク管理者、クラウドアーキテクトを対象としています。認定試験は、プロフェッショナルがAWSセキュリティモデルとFortinetのクラウドセキュリティソリューションについてより深く理解するのを支援します。Fortinet NSE6_WCS-7.0認定は、クラウドセキュリティのキャリアを進め、分野での認知度を高めたいプロフェッショナルにとって価値のある資格です。
質問 # 14
Your company deployed a FortiSandb0X for AWS.
Which statement is correct about FortiSandbox for AWS?
- A. FortiSandbox for AWS does not need more resources because it performs only management and analysis tasks.
- B. The FortiSandbox manager is installed on AWS platform and analyzes the results of the sandboxing process received from on-premises Windows instances.
- C. FortiSandbox for AWS comes as hybrid solution. The FortiSandb0X manager is installed on-premises and analyzes the results Of the sandboxing process received from AWS EC2 instances
- D. FortiSandbox deploys new EC2 instances with the custom Windows and Linux VMS, then it sends malware, runs it, and captures the results for analysis.
正解:A
質問 # 15
Which three statements are correct about Amazon Web Services networking? (Choose three.)
- A. You can use unicast the FGCP protocol
- B. You cannot use custom frames in AWS
- C. You can configure instant IP failover in AWS.
- D. You cannot deploy FortiGate in transparent mode in AWS.
- E. You cannot configure gratuitous ARP but you can configure proxy ARP.
正解:A、B、D
質問 # 16
Which statement is true about an Elastic Network Interface (ENI)?
- A. Once ENI detaches from one instance. it cannot reattach to another instance.
- B. You can detach primary ENI from an AWS instance.
- C. An ENI cannot move between AZs.
- D. When youmove an ENI, network traffic is not redirected to the new instance.
正解:C
質問 # 17
Which three statements are correct about VPC flow (Choose three.)
- A. Flow logs do not capture traffic to andfrom169.2 54 .169.254 for instance metadata.
- B. Flow logs can capture traffic to the reserved IP address for the default VPC router.
- C. Flow logs can be used as a security tool to monitor the traffic that is reaching the instance.
- D. Flow logs do not capture DHCP traffic.
- E. Flow logs can capture real-time log streams for the network interfaces.
正解:A、C、D
質問 # 18
An administrator has deployed an environment in AWS and is now trying to send outbound traffic from the web servers to the internet through FortiGate. The FortiGate policies are configured to allow all outbound traffic. however. the traffic is not reaching the FortiGate internal interface.
Which two statements Can be the reasons for this behavior? (Choose two)
- A. AWS source destination checks are enabled on the FortiGate internal interfaces.
- B. AWS security groups are blocking the traffic.
- C. FortiGate is not configured as a default gateway tor web servers.
- D. Internet Gateway (IGW) is not configured for VPC.
正解:A、B
質問 # 19
A customer deployed Fortinet Managed Rules for Amazon Web Services (AWS) Web-Application Firewall (WAF) to protect web application servers from attacks.
Which statement about Fortinet Managed Rules for AWS WAF is correct?
- A. It can provide Layer 7 DOS protection.
- B. It offers a negative security model.
- C. It can provide IP Reputation (WAF subscription FortiGuard).
- D. It can perform bot and known search engine identification and protection
正解:D
質問 # 20
You connected to the AWS Management Console at 10:00 AM and verified that there are two FortiGate VMS running, You receive a call from a user reporting about a temporary slow Internet connection that lasted only a few minutes. When you go back to the AWS portal. you notice there are now two additional FortiGate VMS that you did not create. Later that day, the number of VMS returns to two without your intervention. A similar situation occurs several times during the week.
What is the most likely reason for this to happen?
- A. Autoscaling is configured to act as described in the scenario.
- B. The user ran a script to create the extra VMS to get faster connectivity.
- C. The AWS portal is not refreshed automatically. and another administrator is creating and removing the VMS as needed.
- D. The VMS are in an availability group with dynamic membership.
正解:A
質問 # 21
A customer deployed an HA Cloud formation to Stage and bootstrap the FortiGate configuration.
Which AWS functions are used by FortiGate HA to call the HA failover?
- A. AWS DynamoDB functions
- B. AWS Lambda functions
- C. AWS S3 functions
- D. AWS Mapping functions
正解:B
質問 # 22
Which AWS product integrates With FortiGate to automate security remediation for workloads running on the AWS platform?
- A. AWS Inspector
- B. AWS Shield
- C. AWS Protector
- D. AWS GuardDuty
正解:D
質問 # 23
An MSSP deployed 16 FortiGate VMS With the default AWS security groups and network access lists using an on-demand license from Amazon Web Services (AWS) Marketplace. They are using a third- party configuration backup application to back up and track changes for the FortiGate configurations. It can connect to the FortiGatedevices using only the SSH protocol, A customer is using the correct username and password configured on the FortiGate devices. but they are unable to log in using the SSH protocol.
What can be the reason Why this authentication is failing?
- A. The default AWS Security group for FortiGate does not allow SSH.
- B. The AWS key is required to log in to FortiGate using SSH
- C. The default AWS network access list for FortiGate does not allow SSH.
- D. AWS uses non-standard SSH port1025, and the default AWS security groups and NACL for FortiGate are not configured for the port.
正解:B
質問 # 24
You are network connectivity issues between two VMS deployed in AWS. One VM is a FortiGate located on subnet *LAN- that is part Of the VPC "Encryption". The Other VM is a Windows server located on the subnet "servers" Which is also in the "Encryption" VPC. You are unable to ping the Windows server from FortiGate.
What is the reason for this?
- A. You have not created a VPN to allow traffic between those subnets.
- B. The default AWS Network Access Control List (NACL) does not allow this traffic.
- C. The firewall in the Windows VM is blocking the traffic.
- D. By default. AWS does not allow ICMP traffic between subnets.
正解:C
質問 # 25
Refer to the exhibit.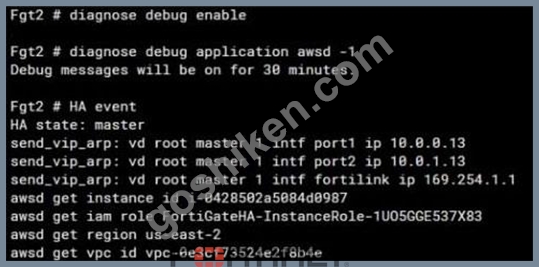
You deployed an active-passive FortiGate HA using a Cloud Formation template on an existing VPC_Now you want to test active-passive FortiGate HA failover by running a debug so you can see the API calls to change the elastic and secondary IP addresses.
Which statement is correct about the output of the debug?
- A. The routing table for Fgt2 updated successfully. and port2 will provide internet access to Fgt2.
- B. The elastic IP is associated with port1of Fgt2.
- C. The elastic IP is associated with port2 of Fgt2. and the secondary IP address for port1and port2 was updated successfully.
- D. IP address 10. O. O. L 3 is now associated with eni-Ob61d8afcOaefb8a2.
正解:D
質問 # 26
......
信頼できるFortinet NSE 6 NSE6_WCS-7.0問題集PDF2024年12月23日最近更新された問題:https://www.goshiken.com/Fortinet/NSE6_WCS-7.0-mondaishu.html
最新NSE6_WCS-7.0試験問題集には合格保証付きます:https://drive.google.com/open?id=1-AxH8lWs95JkdNS2DT2z8zjgTk37t568